The Next Outage Is Already Scheduled

Somewhere in your Azure subscriptions, a secret is about to expire. You just don't know which one.

CertifyClouds finds it before it breaks.

Find Your Expiring Secrets

Runs in your own Azure tenant • Secret values never reach CertifyClouds

1 in 10
enterprises hit a certificate outage every single week
$14,056
average cost per minute of unplanned IT downtime
292
days average to identify and contain a breach involving stolen credentials

Architecture

How It's Built, and Why

Your Secrets Never Reach Us

The Key Vault Scan reads metadata only. New credentials from a rotation are never sent to CertifyClouds. They go only where you configure, such as your Key Vaults and the AWS or GCP copies you set up.

Self-Hosted In Your Network

Runs as a Docker container in your Azure subscription. Data is stored in your infrastructure; optional integrations connect only when your administrator enables them.

Not Another Vault

Works with the Key Vaults you already have. No migration. No new secrets store. No vendor lock-in.

Managing Azure Secrets Shouldn't Be This Hard

Secrets Expire Without Warning

You find out a secret expired when production breaks. By then, it's already a 3 AM incident with the whole team on a call.

Rotation Is Tedious & Risky

Manual rotation means touching 5 different systems, hoping you don't miss one, and praying the app doesn't break.

No Single Source of Truth

"Who rotated this secret?" "When does it expire?" "Which apps use it?" Nobody knows. The person who set it up left 2 years ago.

Manual Process vs. CertifyClouds

See how much time and risk you can eliminate.

Task
Manual Process
With CertifyClouds
Find expiring secrets across all vaults
2-4 hoursClick through each vault in Azure Portal
Minutes, not hoursOne scan across every connected subscription
Rotate an App Registration secret
15-30 min5+ systems to update, hope you don't miss one
One clickRotates the credential and updates the App Services, Function Apps, Container Apps, Logic Apps, SQL servers, and Azure DevOps service connections and variable groups that use it
Generate compliance evidence
1-2 daysExport data, build spreadsheets, format report
One clickCurrent-state dashboard plus a PDF evidence bundle on demand
Know if a secret expired right now
When production breaksFind out at 3 AM when apps stop working
Days beforeEmail and webhook alerts at the thresholds you set, for example 30 and 7 days
DR secrets available during Azure outage
NoDR site can't authenticate anywhere
YesAuto-synced to AWS/GCP Secret Manager

We found expired credentials we didn't know existed within the first scan. Rotations that used to take a change ticket and an afternoon now take minutes, and the audit trail is there when security asks.

Platform teamUK logistics group · 2,000+ secrets under management

Discover. Rotate. Sync.

The complete Azure secret lifecycle. From the Key Vault Scan to App Registration rotation to multi-cloud sync.

Key Vault Scan

Discover & Scan Everything

Automatically find all Key Vaults across your subscriptions. Scan secrets, certificates, and keys. See expiration dates, compliance status, and security issues at a glance. The same scan finds the certificates your App Services, Application Gateways, API Management, Container Apps and Front Door serve on custom domains, so you hear about the one somebody uploaded by hand two years ago before it takes your site down.

  • Scans up to 20 subscriptions
  • Detects expiring secrets before they break
  • TLS endpoint certificates, including ones never stored in Key Vault
  • No access to secret values (metadata only)
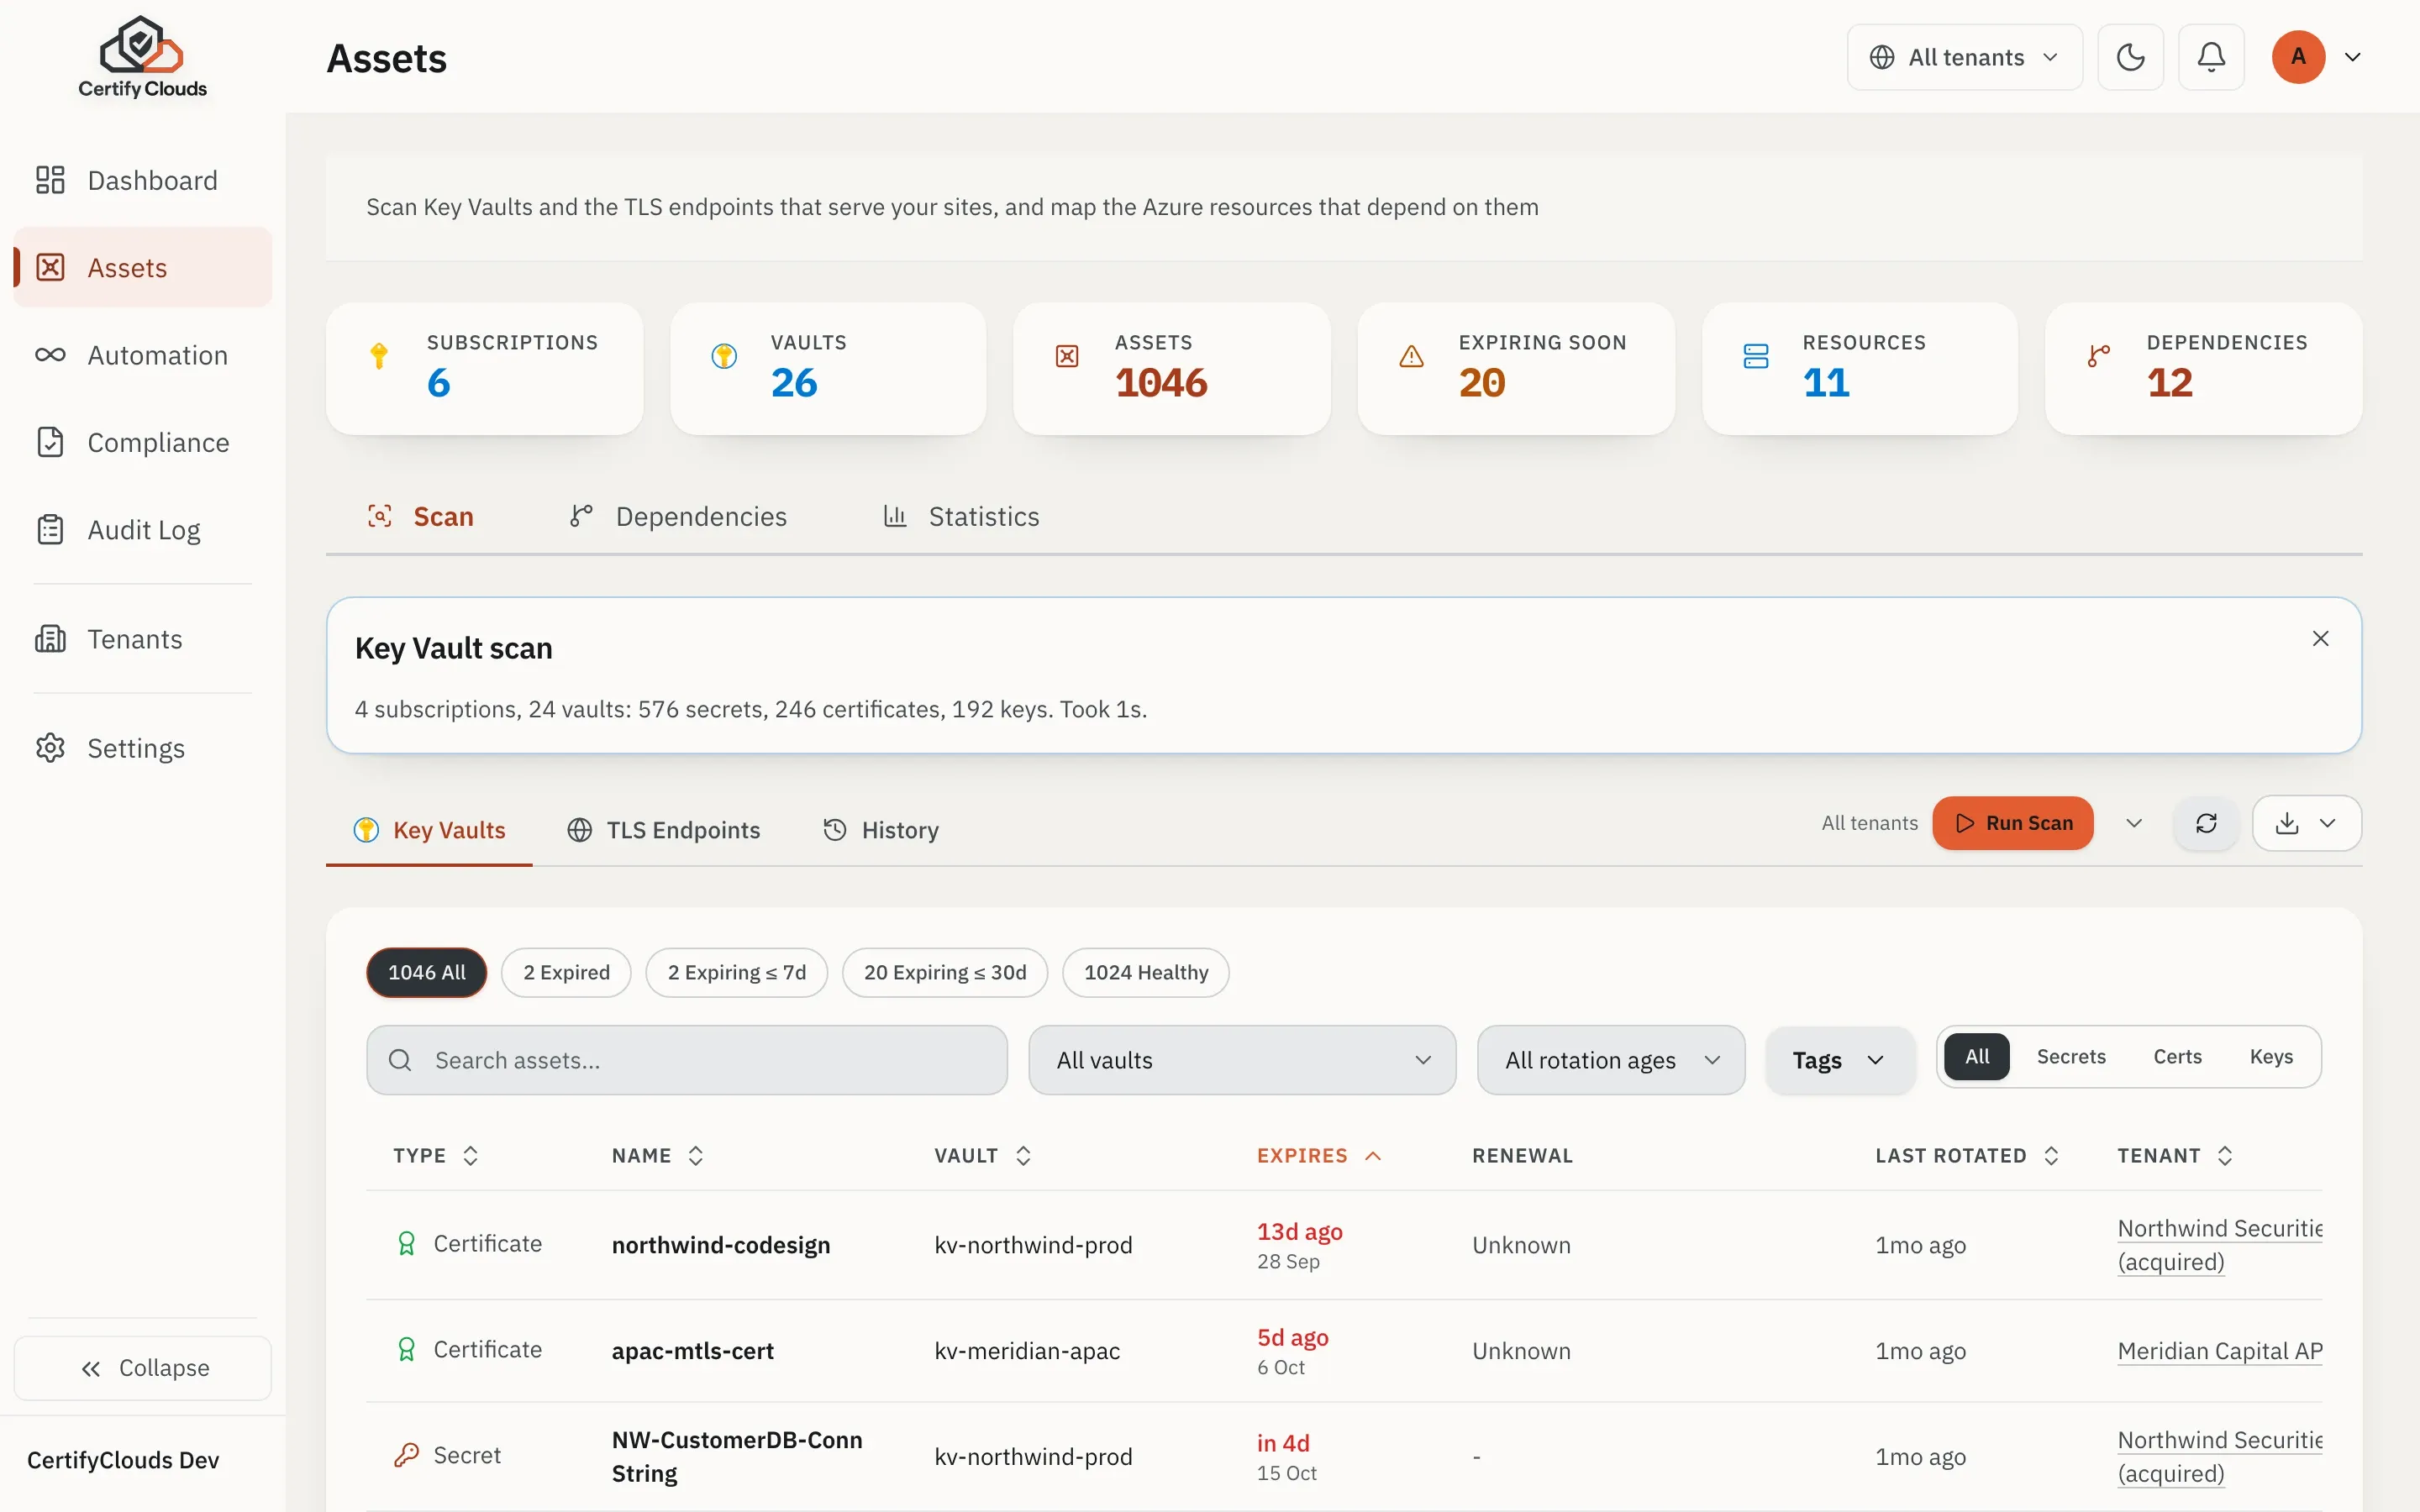
Key Vault Scan: every Key Vault across your subscriptions
Compliance

Continuous Security Scoring

See your current security posture at a glance. Track findings against framework controls. Export evidence packages for auditors.

  • Pre-built compliance rules
  • Flags weak certificate signatures, broken chains and certificates with no renewal or reminder set
  • Trend analysis and reporting
  • Auditor-ready evidence packages (CSV plus PDF bundle with customer management assertion) for CIS Azure, SOC 2, ISO 27001, NIST 800-53, Microsoft cloud security benchmark, HIPAA and PCI DSS*

* CertifyClouds is an evidence aggregator for Azure credential-lifecycle controls. We identify what violates each framework and recommend the fix. We are not a certified compliance product. Read the full disclaimer →
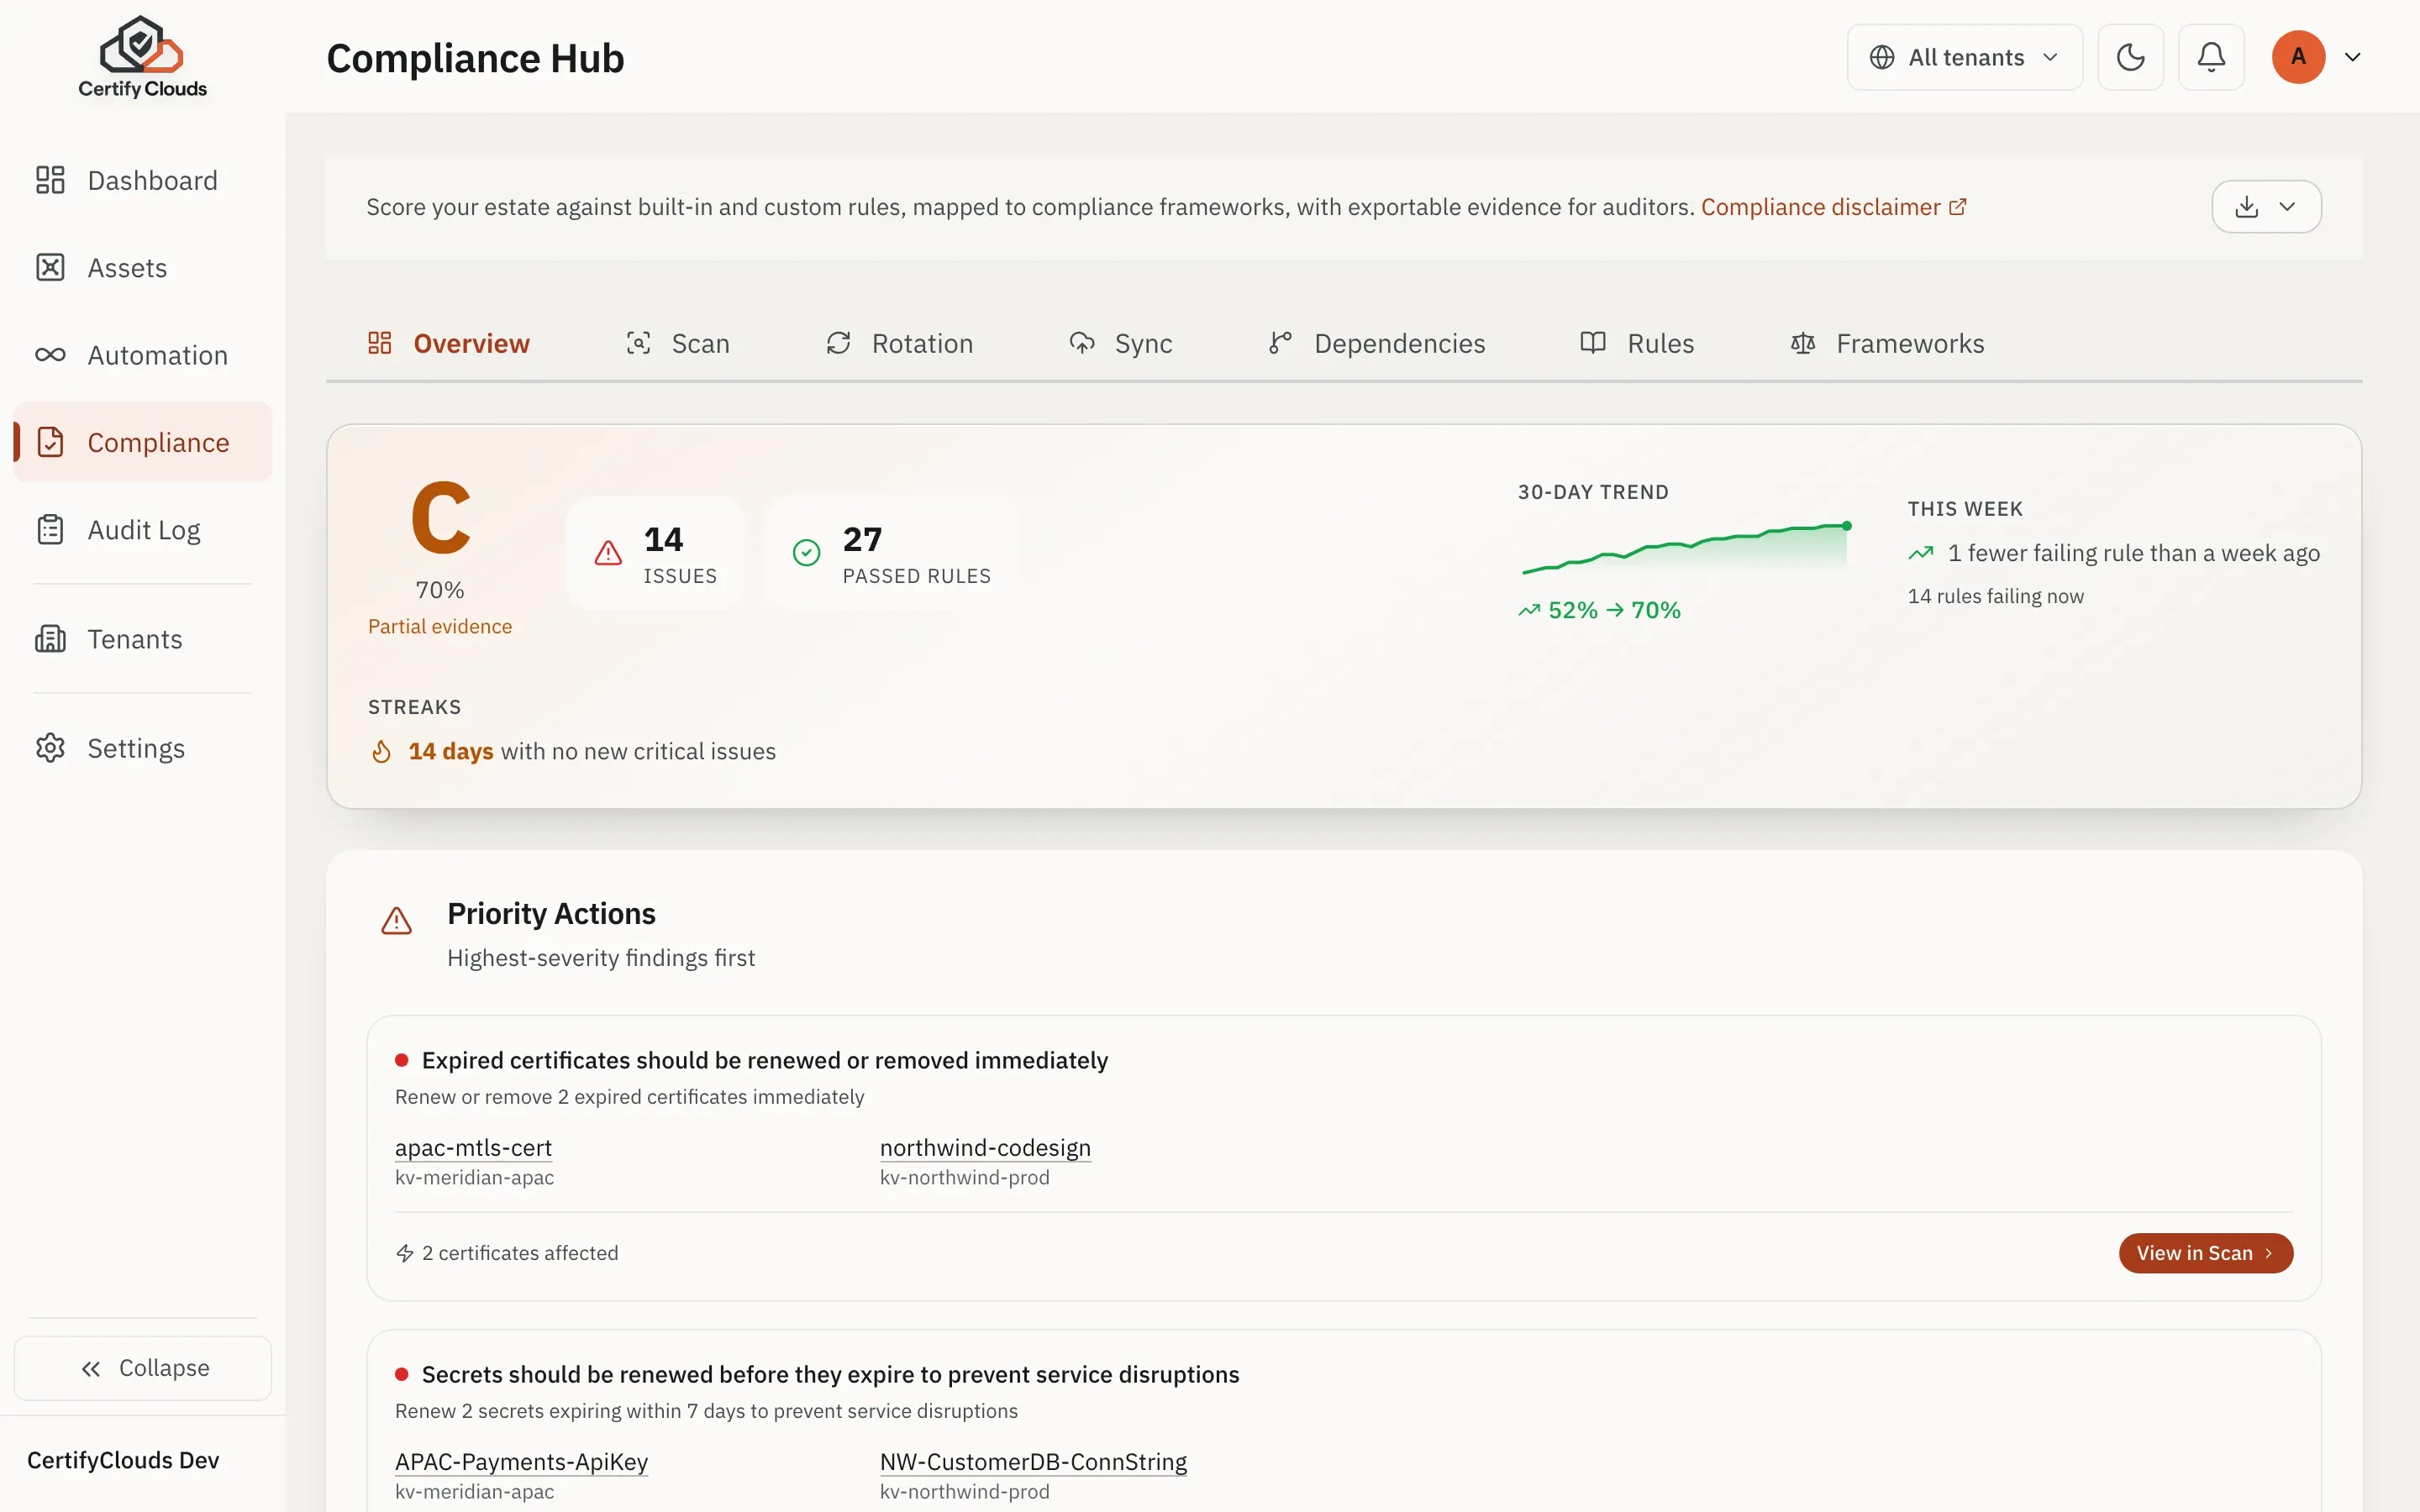
Compliance Hub showing current posture, priority actions, and automated framework evidence
Automation Rotation

Automated Rotation

Rotate App Registration secrets and certificates, then sync to Key Vaults automatically. No more manual rotation.

  • One-click rotation
  • Audit trail for every change
  • Auto-sync to target Key Vaults
  • No Key Vault auto-renewals that break App Registration sign-in
  • CA-issued certificates renewed through their CA
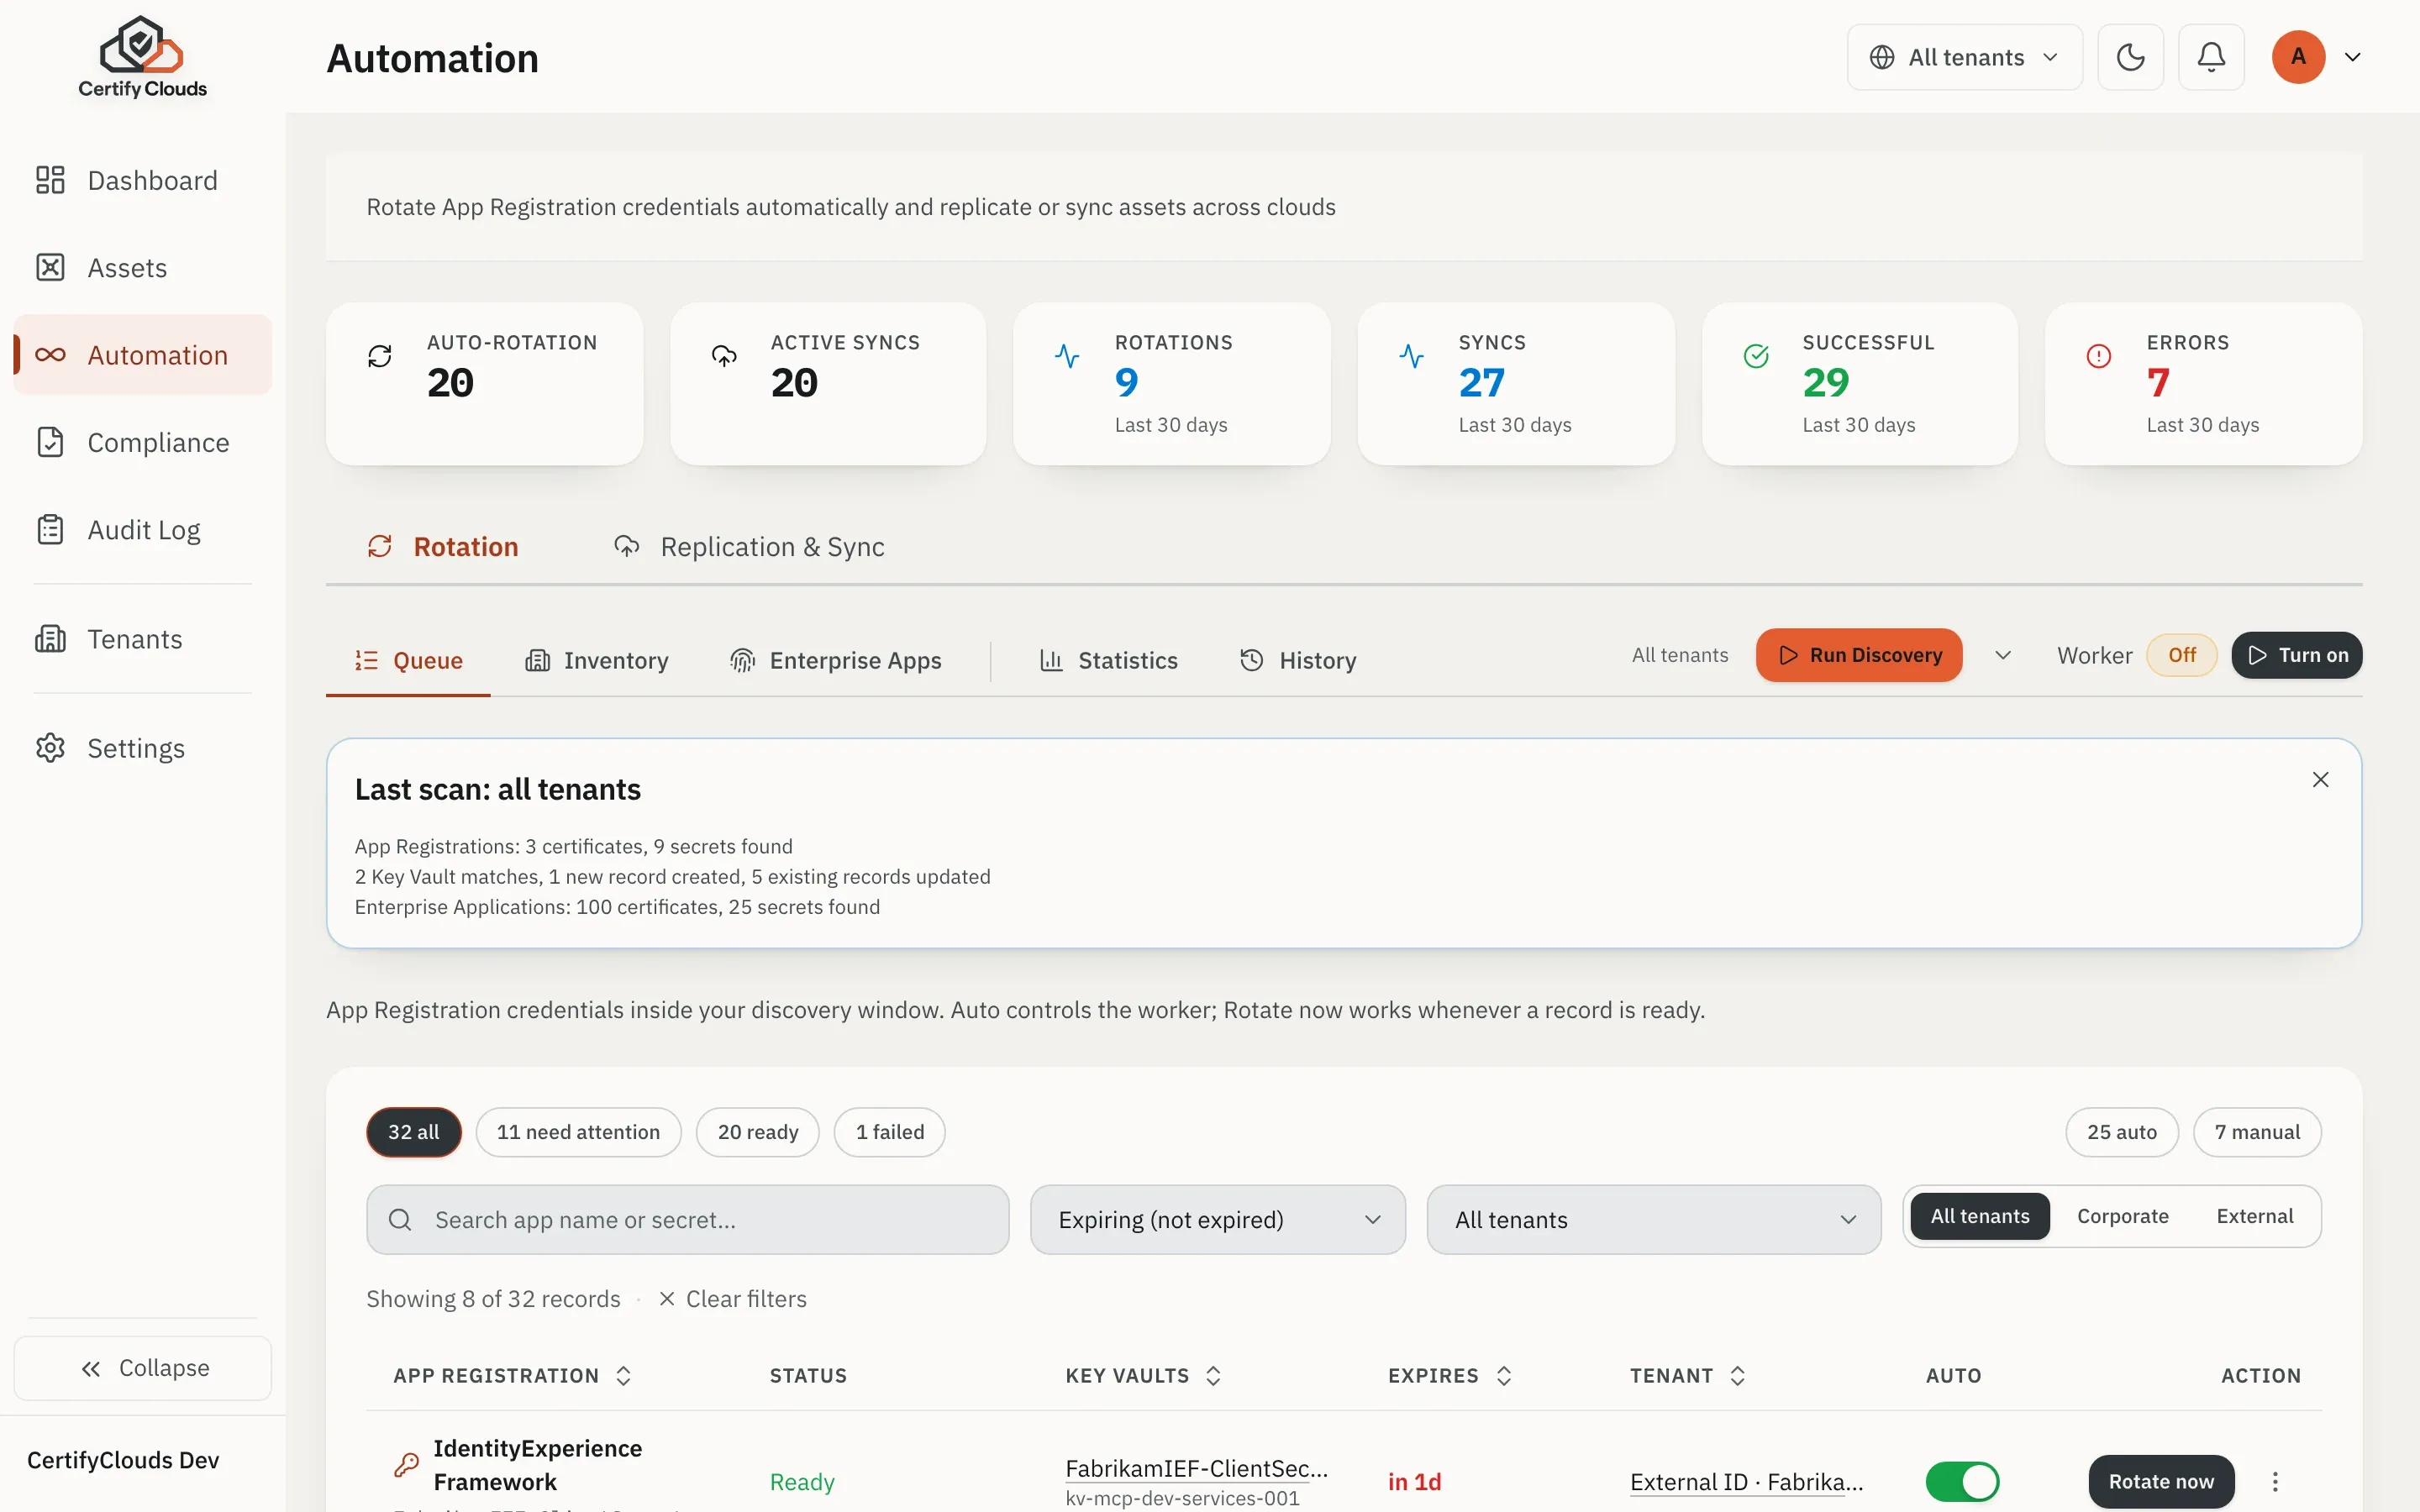
Automation Rotation: App Registration inventory with one-click rotation
Alerts

Never Miss an Expiration

Get notified before secrets expire. Email, webhook, or both.

  • Thresholds you set for each rule
  • Rules for all credentials or one kind, such as Key Vault secrets or TLS endpoints
  • Webhook integration for Slack, Teams, PagerDuty
  • App owners in Entra emailed too, once an admin switches it on
  • Warns your admins before CertifyClouds' tenant and SSO secrets expire
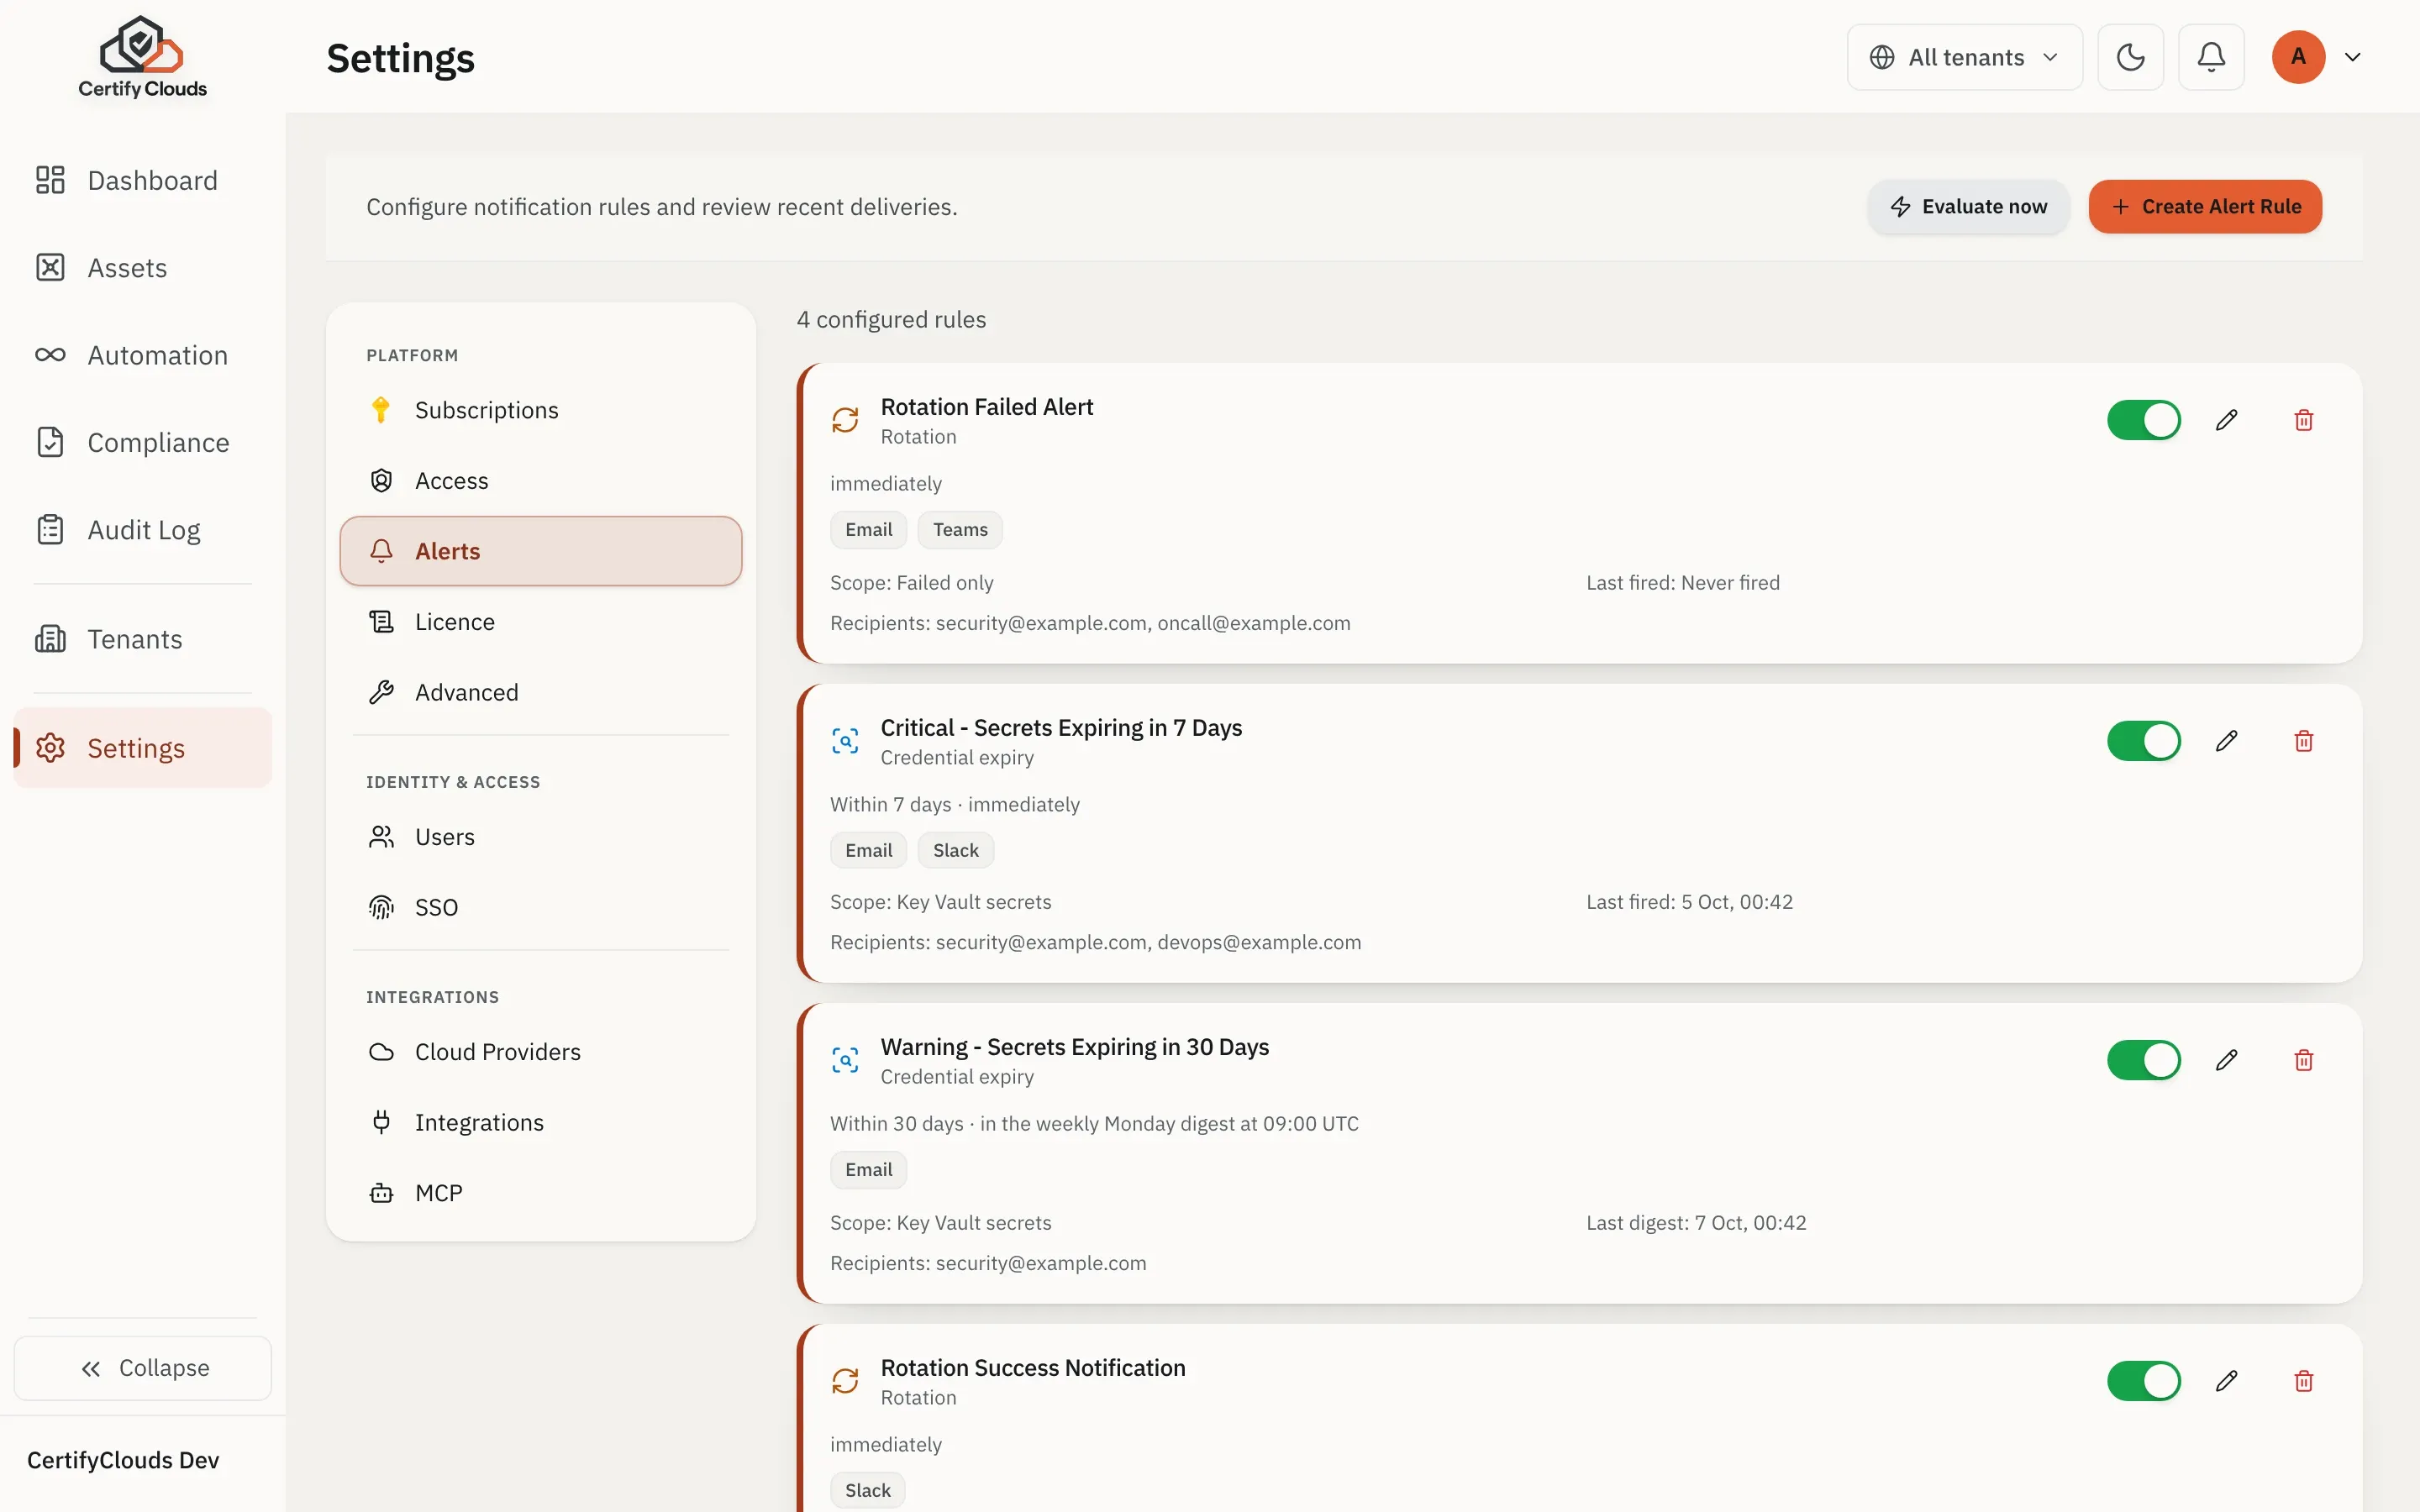
CertifyClouds alert rules: expiry thresholds and webhook integrations
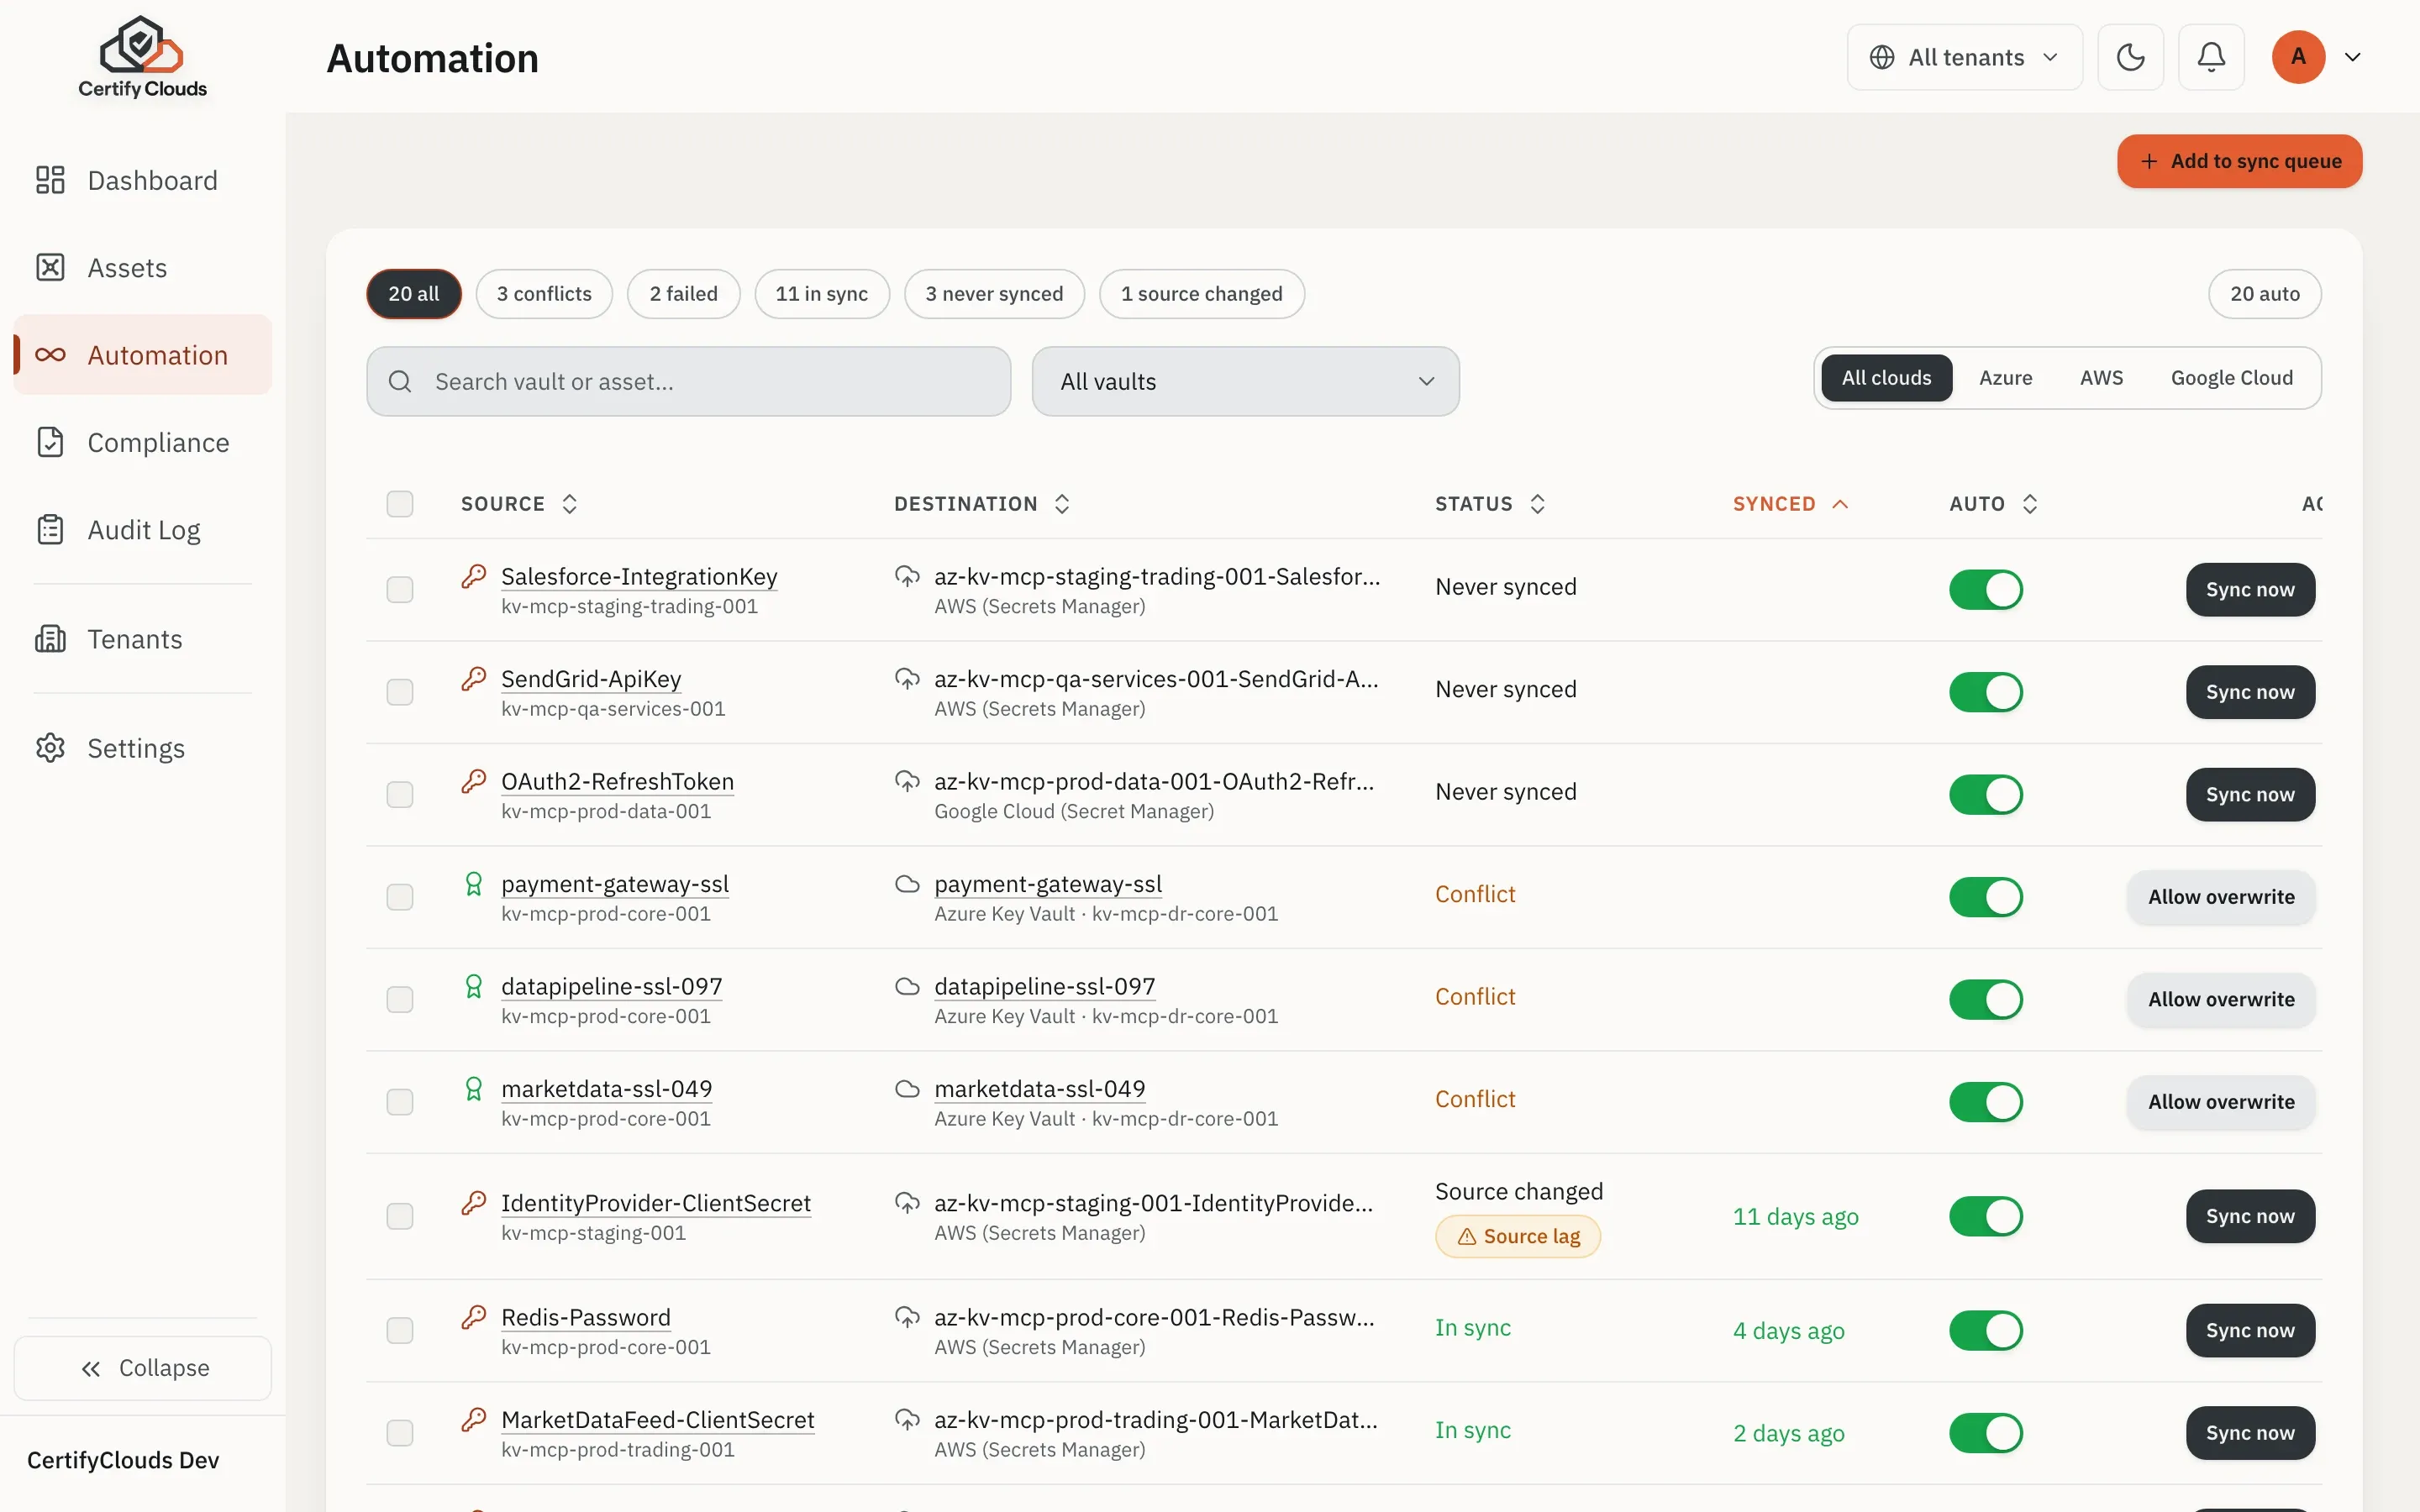
Automation Sync

Multi-Cloud Disaster Recovery

Replicate Azure Key Vault secrets and certificates to AWS and GCP secret and certificate managers. When Azure goes down, your DR environment has the credentials it needs.

  • Sync to AWS Secrets Manager and ACM
  • Sync to GCP Secret Manager and Certificate Manager
  • Copies updated straight after every rotation
  • The old credential waits for its copies before it is retired, up to a limit you set
  • Tag-based secret selection
CertifyClouds multi-cloud sync: AWS Secrets Manager and GCP Secret Manager destinations
Multi-Tenant · Enterprise

Every Tenant, One Console

MSPs, holding groups, and post-acquisition estates run credentials across many Microsoft Entra ID tenants. Register them all in one CertifyClouds deployment and discover, rotate, and report across the whole estate without switching directories.

  • Cross-tenant inventory and rotation from a single console
  • Per-tenant connection health and scan status
  • Azure AD B2C and Entra External ID tenants alongside your corporate directories
  • Key Vault to Key Vault replication for regional DR and environment sync
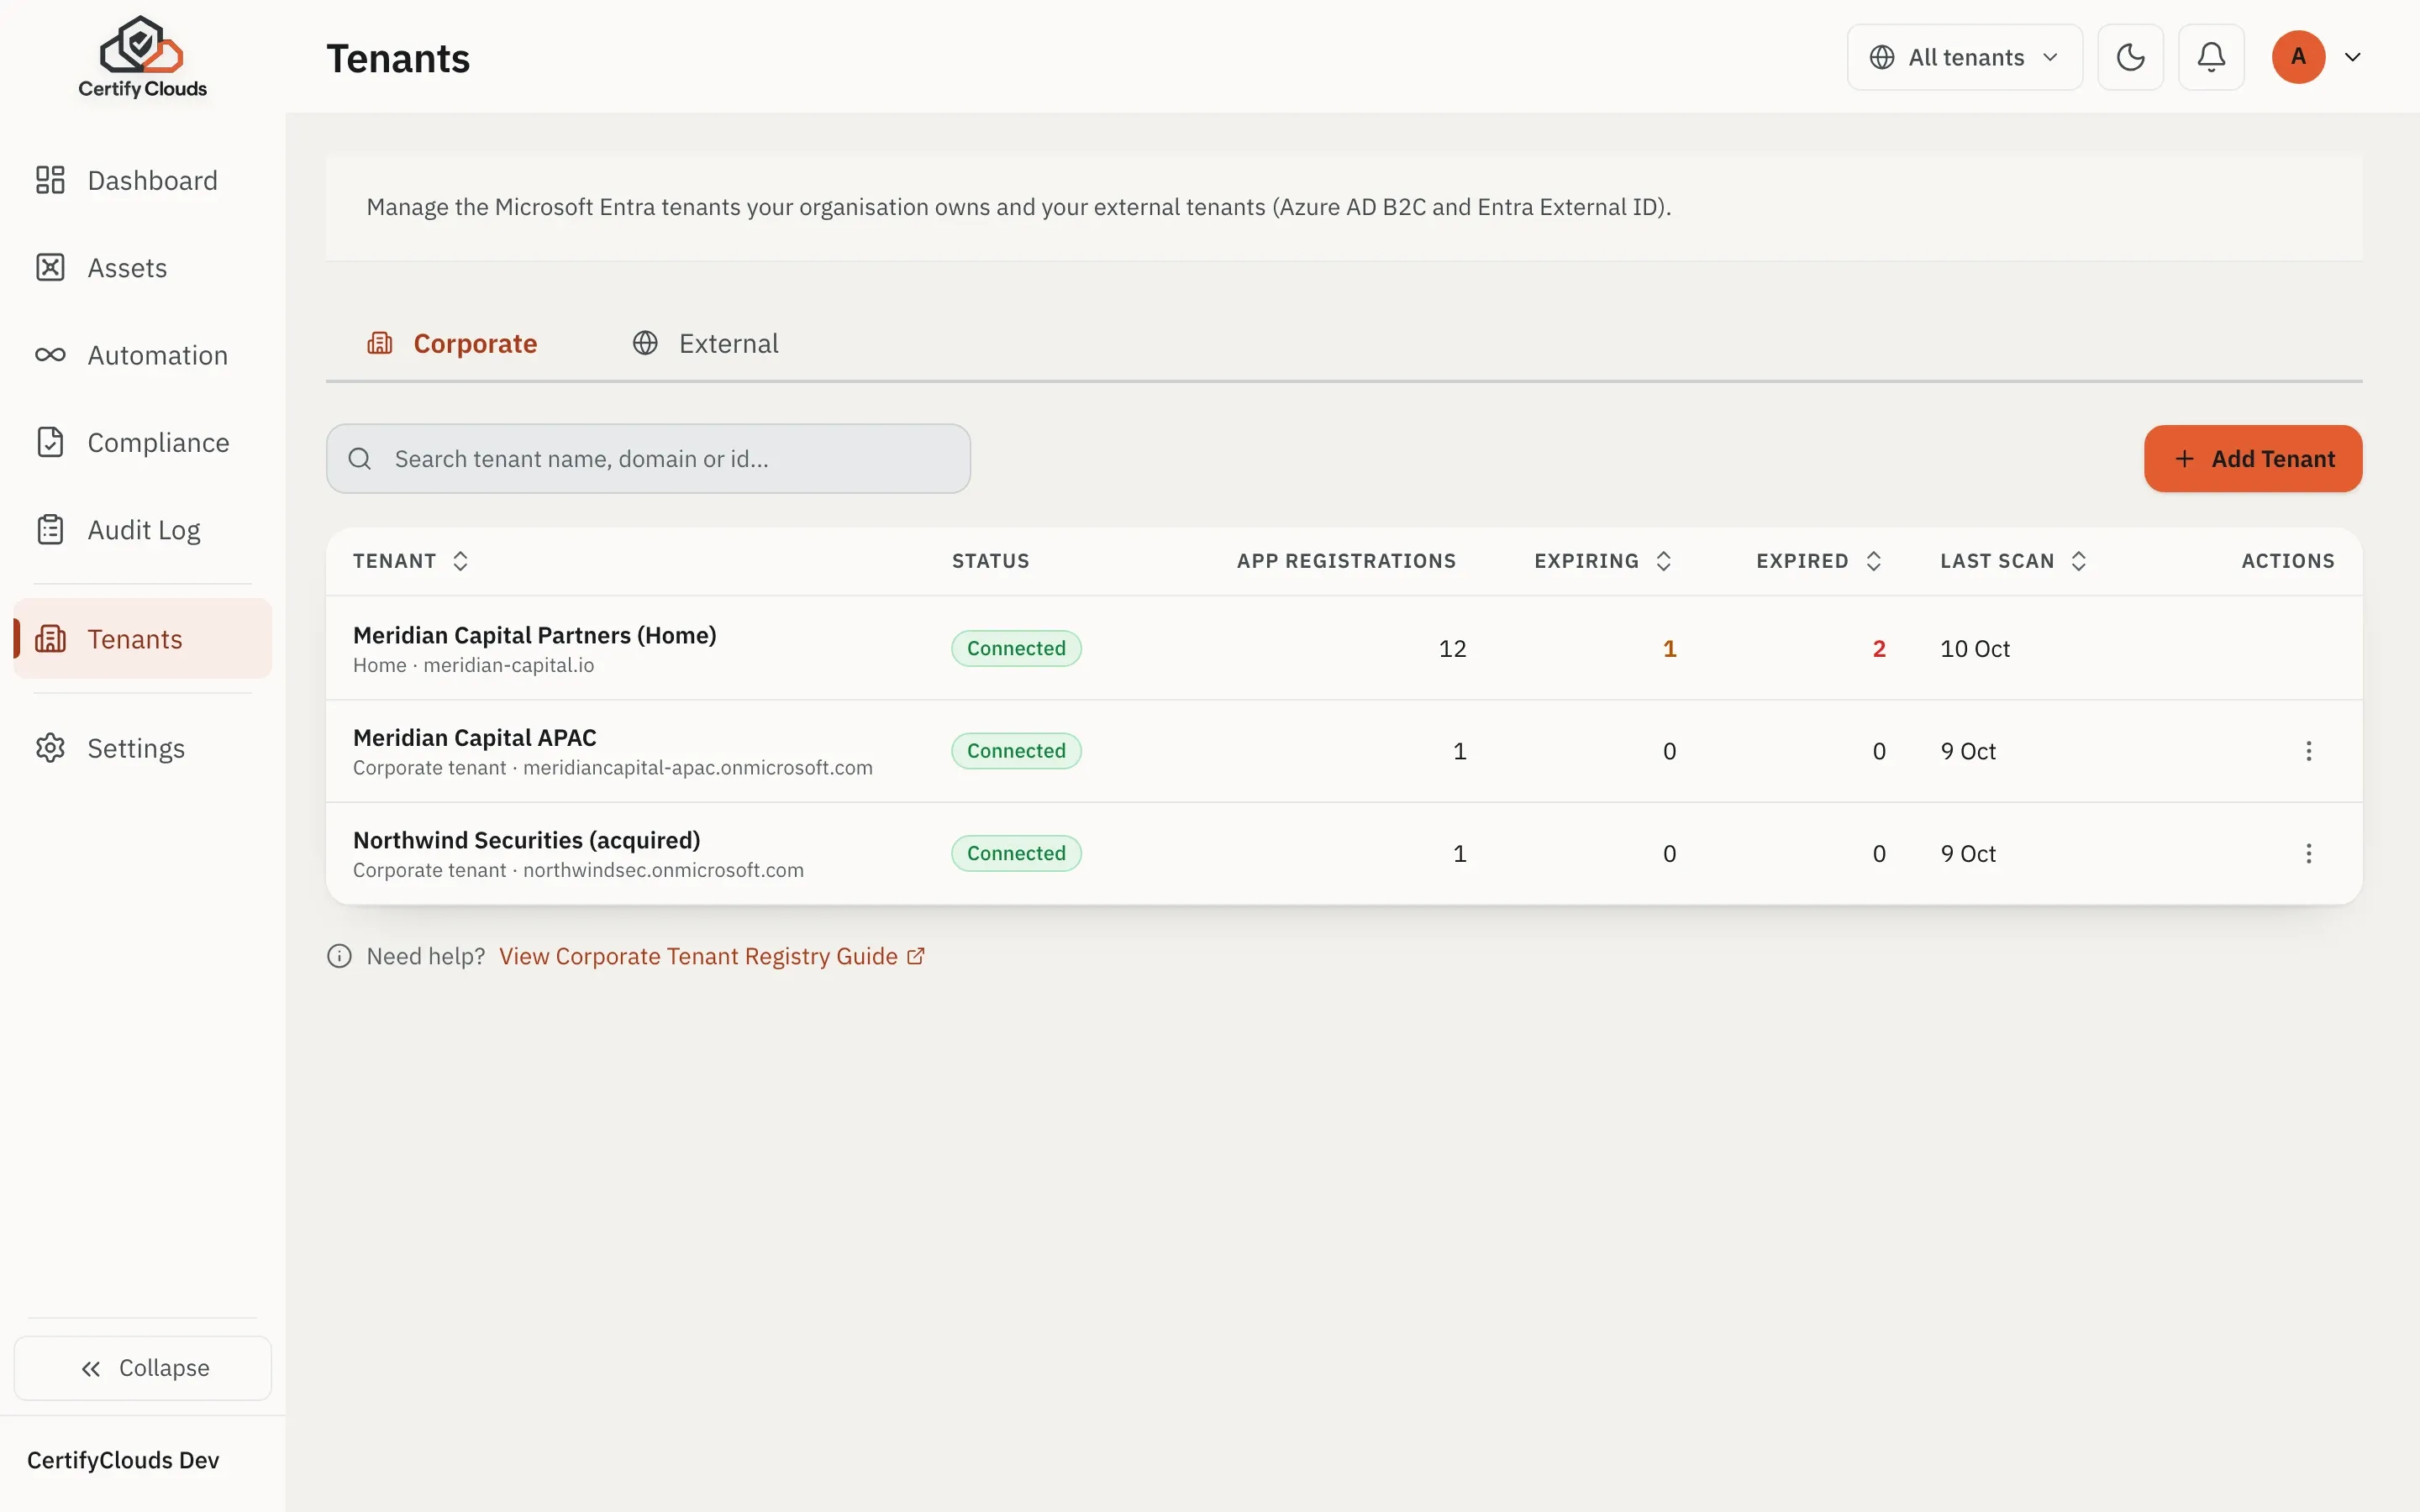
Tenants page: cross-tenant inventory with per-tenant connection health

Alerts and notifications, wherever your team already works

How It Works

CertifyClouds runs entirely in your environment. Your secret values never reach CertifyClouds.

1

Connect Your Azure

Grant read-only access with our setup script. Settings → Access then shows exactly what CertifyClouds can reach.

2

Run Your First Scan

Discover all Key Vaults and secrets across your subscriptions.

3

Get Compliant

Review issues, set up alerts and turn on automatic rotation.

V1.8 Live

What's New and Next

Entra External ID tenants and cross-tenant management are now live, alongside the read-only MCP Connector for hosted ChatGPT and Claude.ai. The 1.8.0 release adds TLS endpoint monitoring, certificate checks (how each one renews, weak signatures, broken chains), certificate renewal through your own CA, copies in AWS and Google Cloud updated on every rotation, a view of exactly what CertifyClouds can access in your tenant, and monitoring of Enterprise Application credentials. Planned next: SAML sign-in, sync to self-hosted secret managers and AKS workload discovery.

View Full Roadmap
LiveTLS Endpoint Monitoring
LiveCertificate Intelligence
LiveCopies Updated on Every Rotation

From the Blog

Practical guides on Azure secret management, rotation, and cloud security.

Plans and Pricing

Start with a free 30-day trial.

Choose from Starter, Pro, or Enterprise plans to match your security needs.

View Pricing Plans

Frequently Asked Questions

CertifyClouds uses Azure RBAC with minimal permissions. The Key Vault Scan reads metadata only (names and expiry dates), never secret values. Rotation, sync and replication handle the values of the credentials you choose, inside your deployment, and never send them to CertifyClouds.

CertifyClouds runs as a Docker container in your Azure environment. You control where it runs and what it can access.

Our setup script detects firewalled vaults and guides you through adding exceptions or using private endpoints.

Yes. Start with a free 30-day trial with all features enabled.

Starter includes the Key Vault Scan, TLS endpoint monitoring, monitor-only Enterprise Application credential inventory, compliance dashboard, alerts, and 3 manual rotations per month for up to 4 subscriptions. Pro adds unlimited automated rotation, multi-cloud sync to AWS and GCP with copies updated on every rotation, Asset Dependencies (including which Key Vault certificate each TLS endpoint uses), SSO via OIDC and Microsoft Entra ID (SAML on roadmap), B2C and External ID tenant discovery, up to 20 subscriptions, and priority support. Enterprise is for 21+ subscriptions or custom commercial/support requirements.

Automation Sync replicates your Azure Key Vault secrets and certificates to AWS Secrets Manager, AWS Certificate Manager, GCP Secret Manager, and GCP Certificate Manager for disaster recovery. You choose what to copy by tag, by vault or item by item, with exclusion patterns, and every rotation updates the copies straight away.

Get in Touch

Ask for a demo, a trial or a price.

Let's Talk

Demos, technical questions and Enterprise pricing all come to the same inbox.

We reply within 2 to 4 UK business days, depending on your plan.