Discover. Rotate. Sync.
The complete Azure secret lifecycle. From the Key Vault Scan to App Registration rotation to multi-cloud sync.
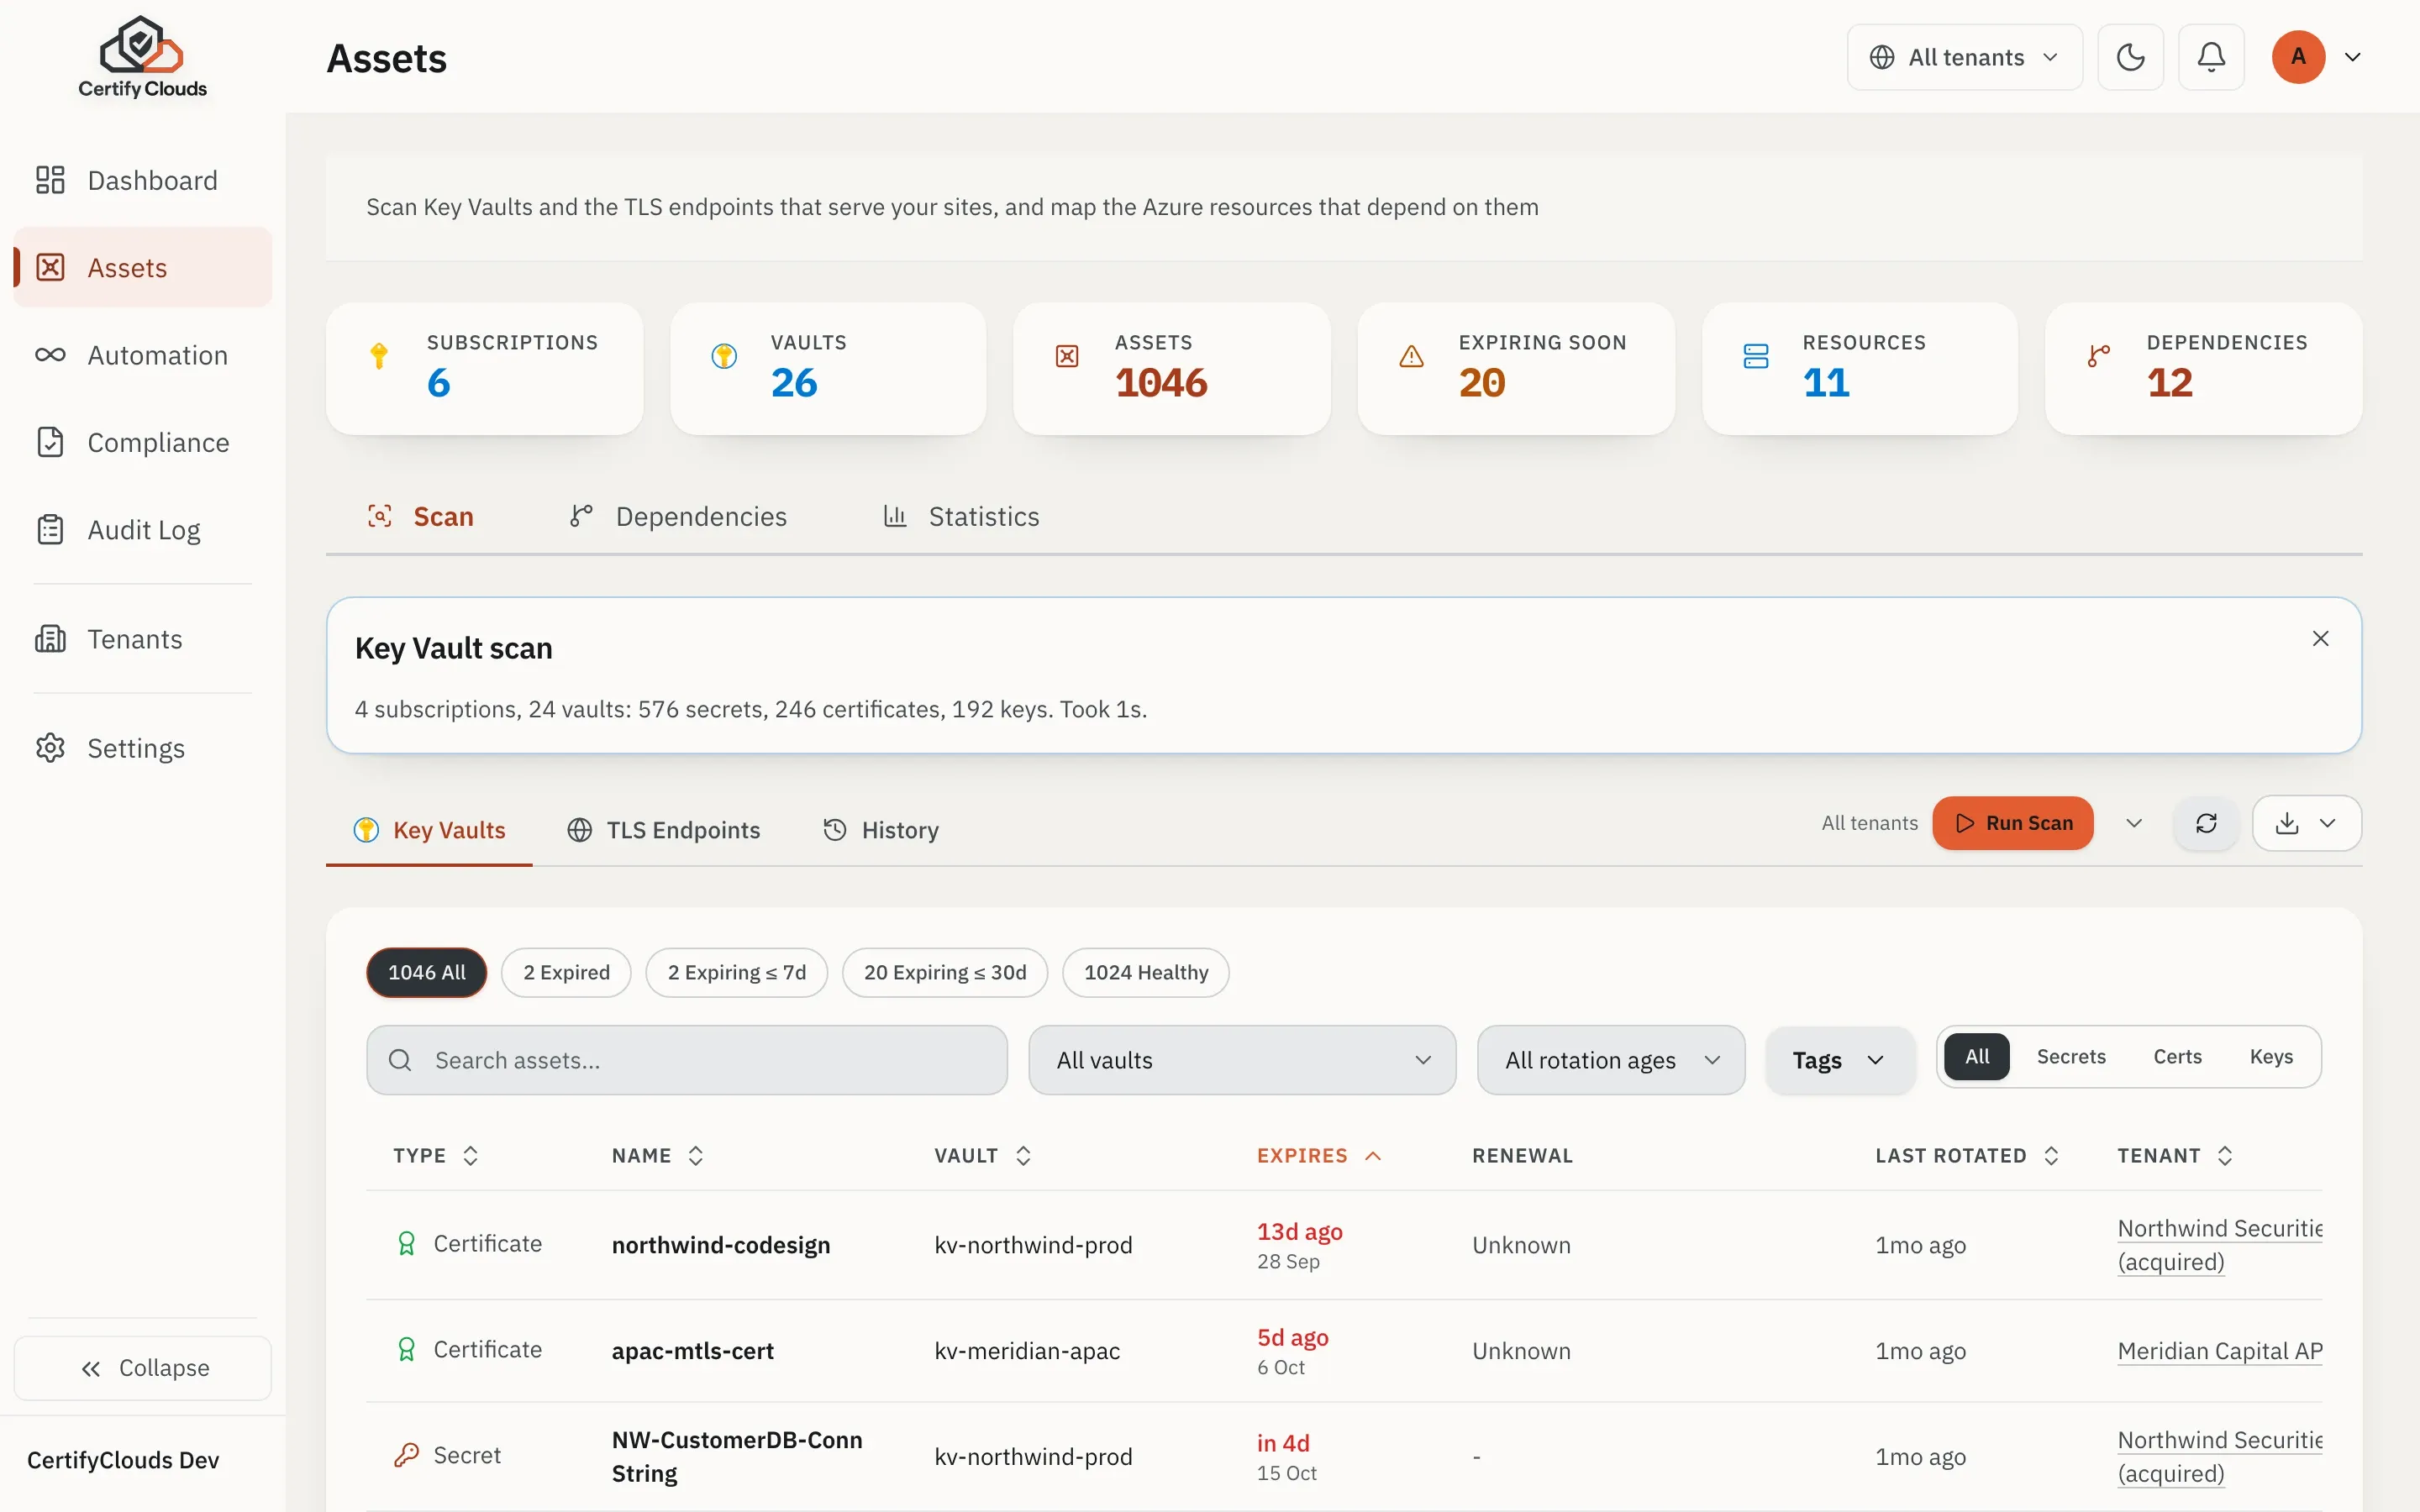
Discover & Scan Everything
Automatically find all Key Vaults across your subscriptions. Scan secrets, certificates, and keys. See expiration dates, compliance status, and security issues at a glance. The same scan finds the certificates your App Services, Application Gateways, API Management, Container Apps and Front Door serve on custom domains, so you hear about the one somebody uploaded by hand two years ago before it takes your site down.
- Scans up to 20 subscriptions
- Detects expiring secrets before they break
- TLS endpoint certificates, including ones never stored in Key Vault
- No access to secret values (metadata only)
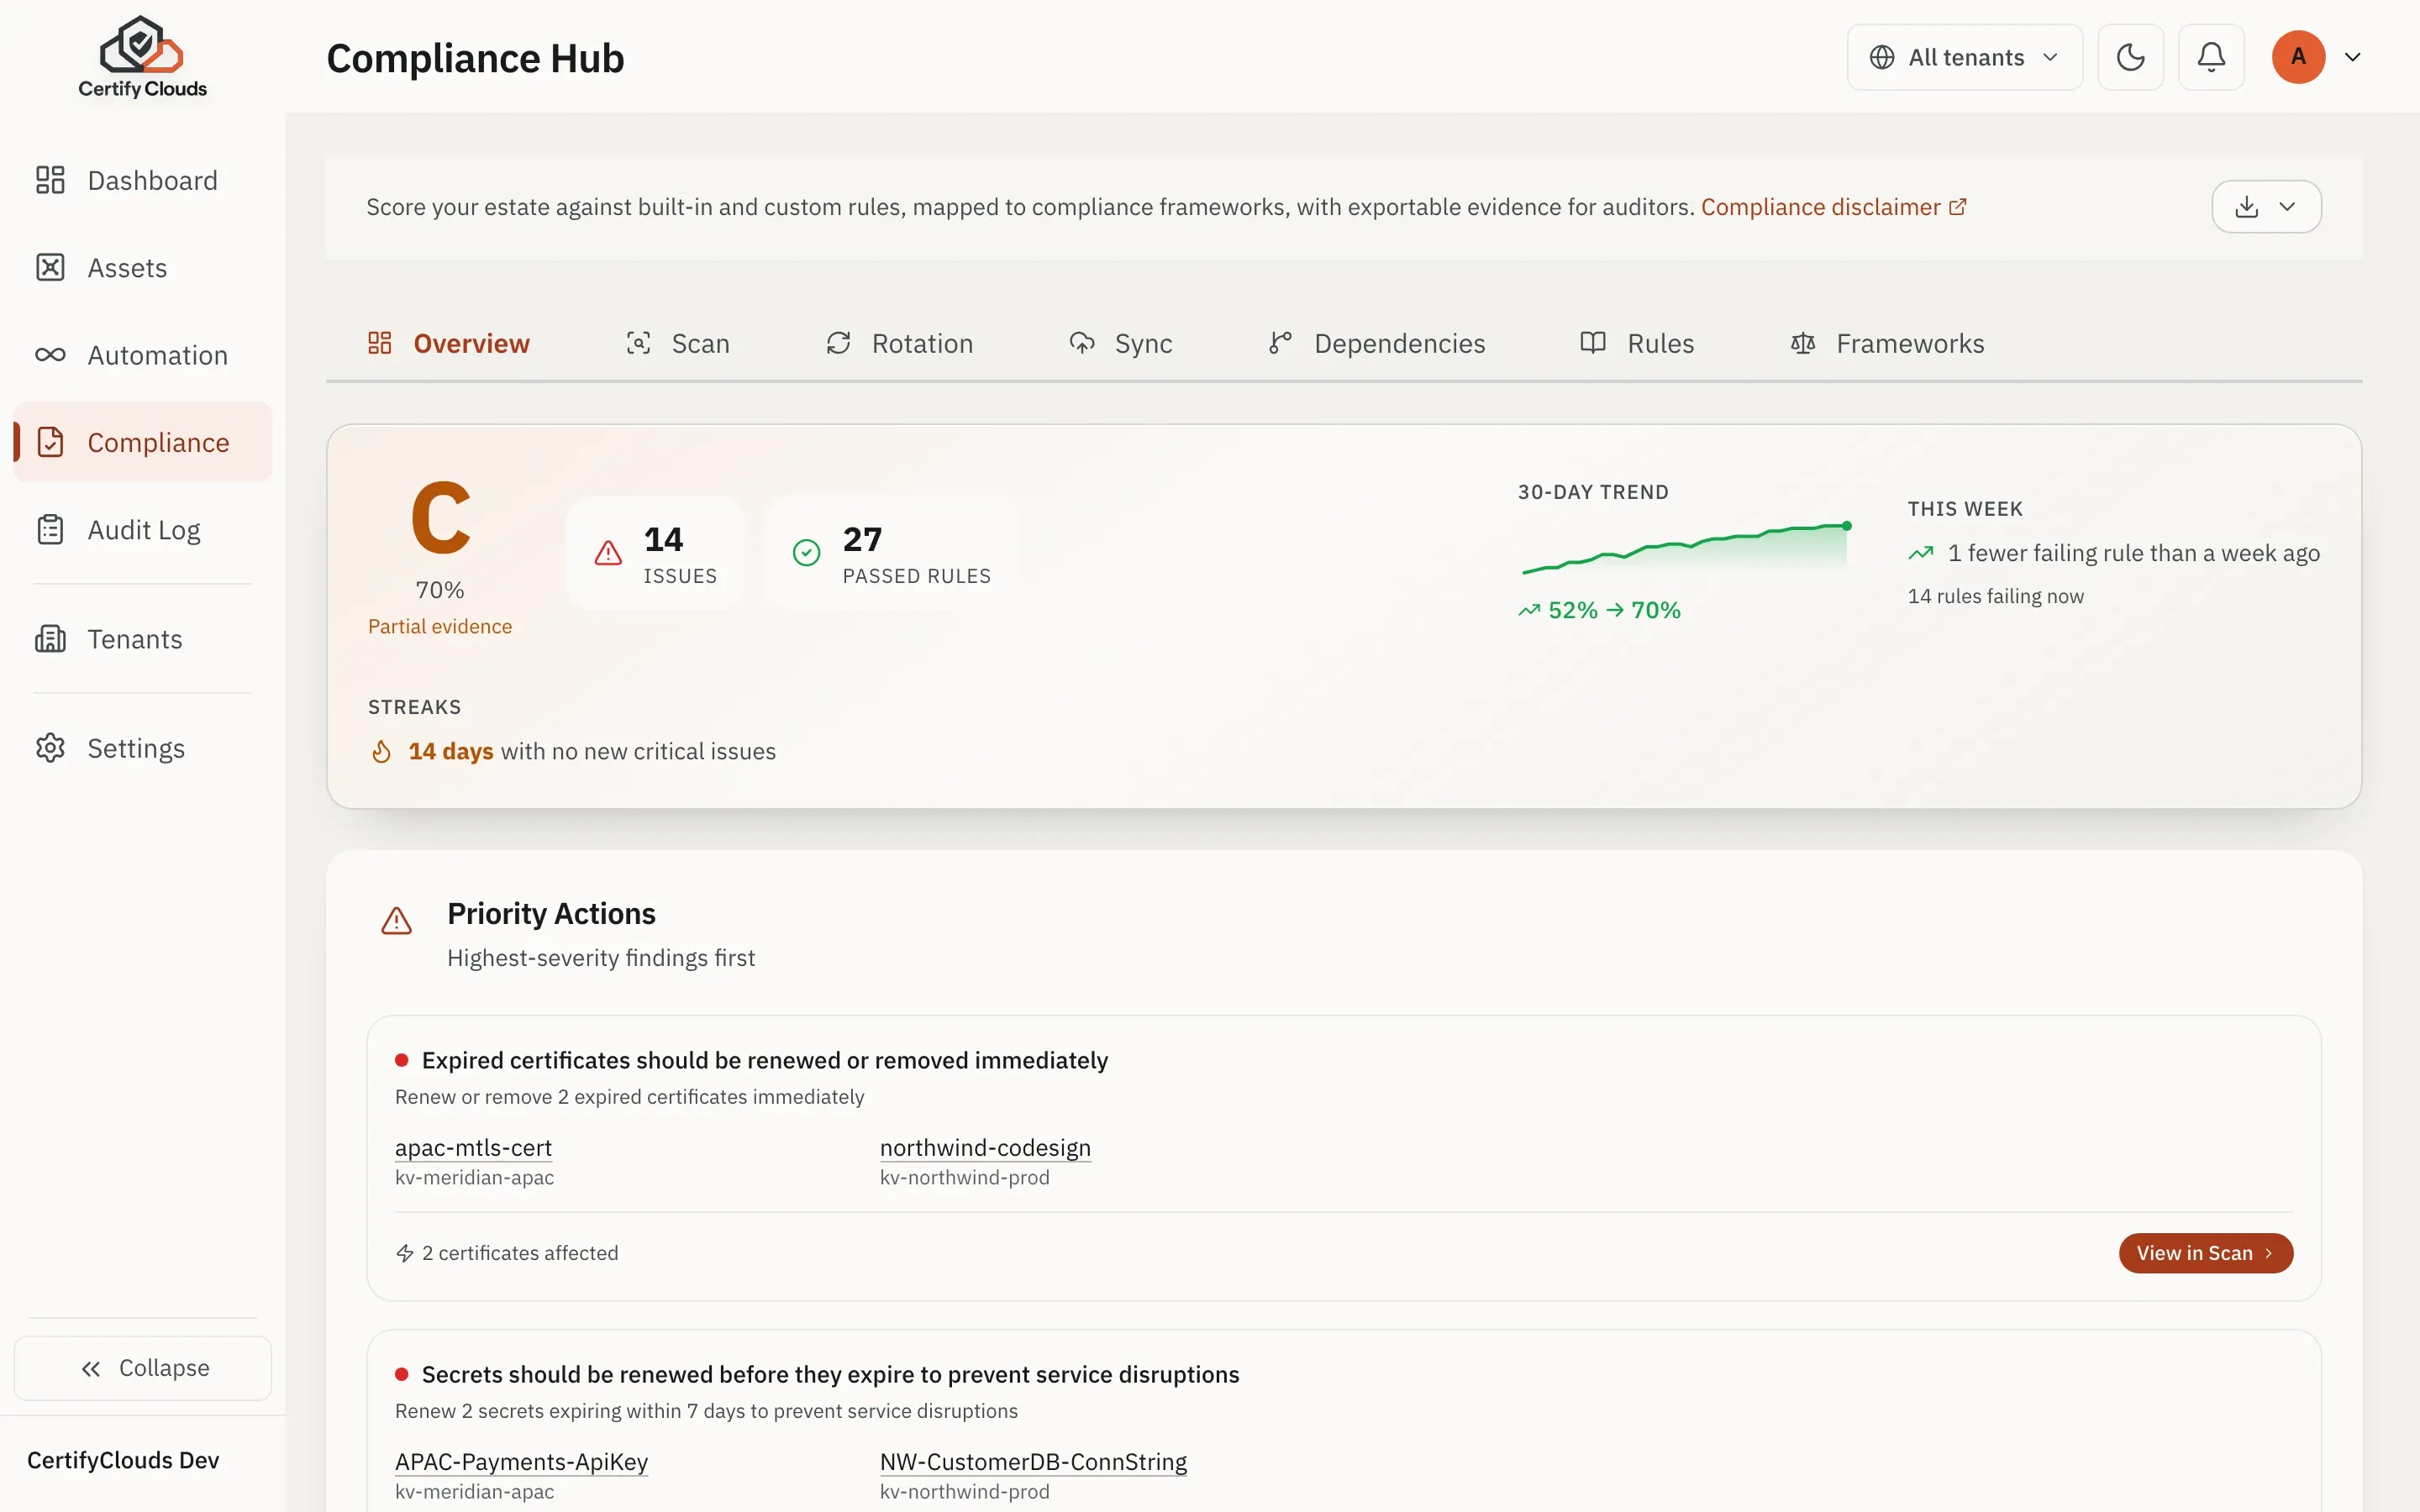
Continuous Security Scoring
See your current security posture at a glance. Track findings against framework controls. Export evidence packages for auditors.
- Pre-built compliance rules
- Flags weak certificate signatures, broken chains and certificates with no renewal or reminder set
- Trend analysis and reporting
- Auditor-ready evidence packages (CSV plus PDF bundle with customer management assertion) for CIS Azure, SOC 2, ISO 27001, NIST 800-53, Microsoft cloud security benchmark, HIPAA and PCI DSS*
* CertifyClouds is an evidence aggregator for Azure credential-lifecycle controls. We identify what violates each framework and recommend the fix. We are not a certified compliance product. Read the full disclaimer →
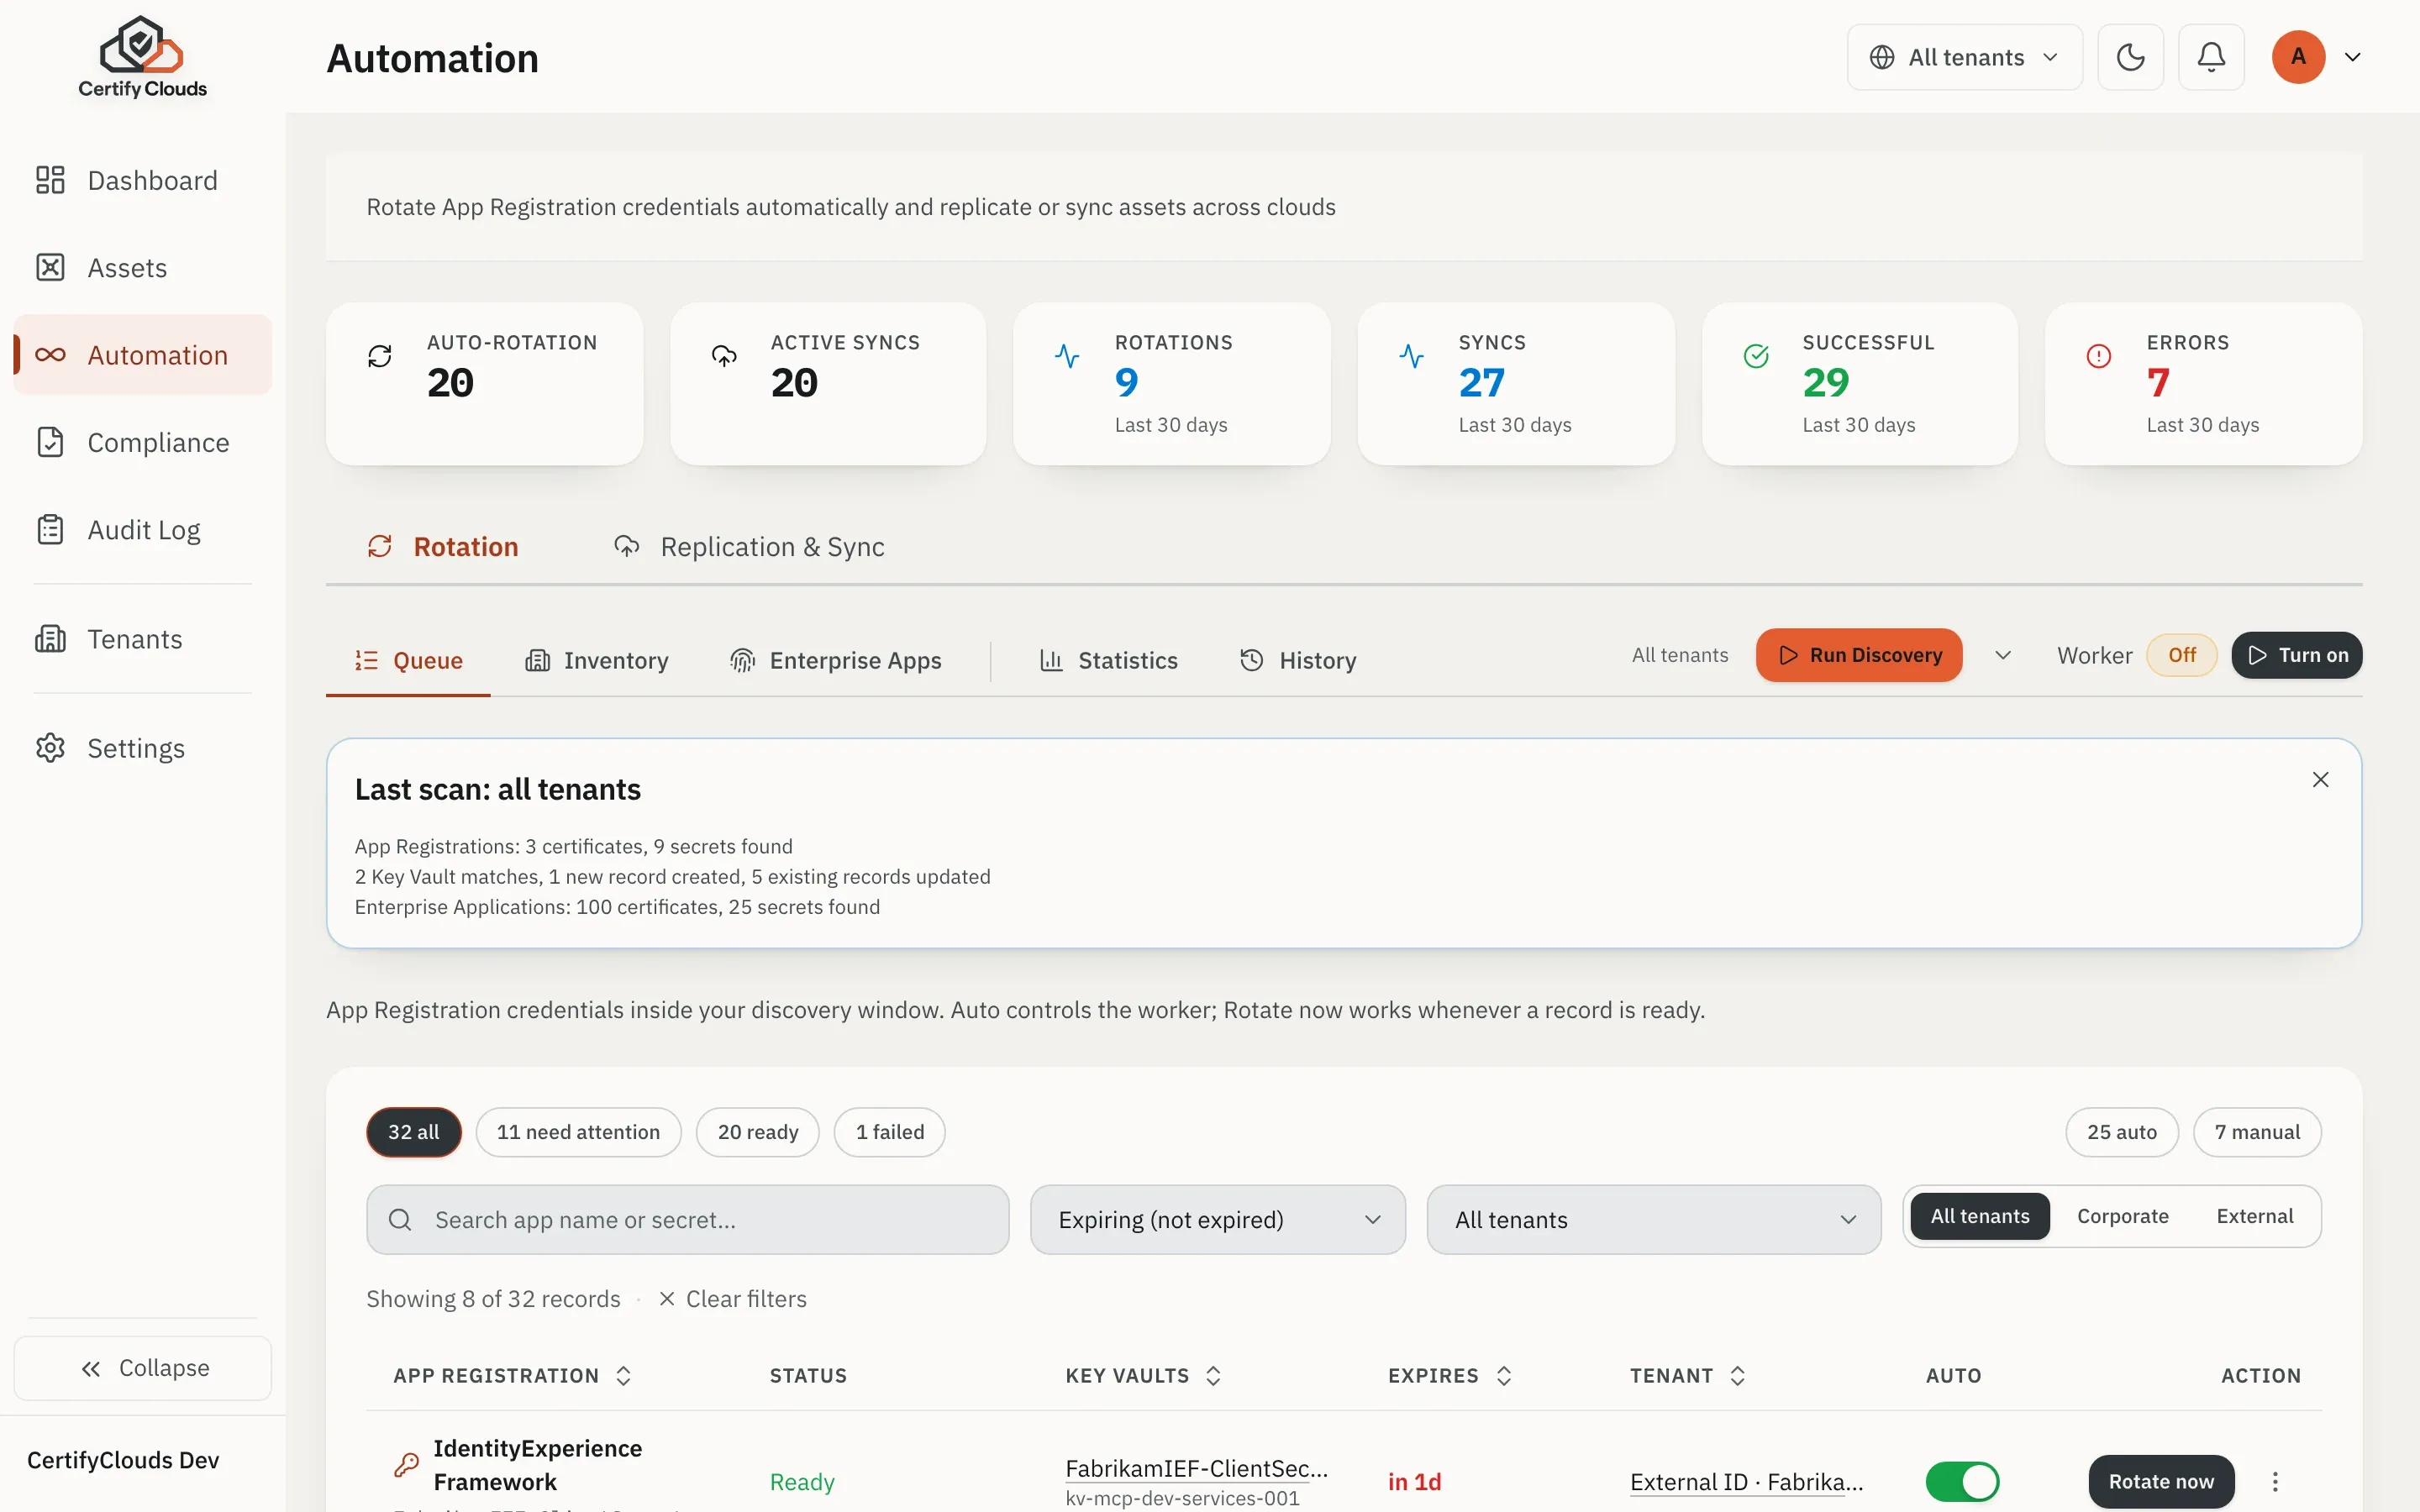
Automated Rotation
Rotate App Registration secrets and certificates, then sync to Key Vaults automatically. No more manual rotation.
- One-click rotation
- Audit trail for every change
- Auto-sync to target Key Vaults
- No Key Vault auto-renewals that break App Registration sign-in
- CA-issued certificates renewed through their CA
Never Miss an Expiration
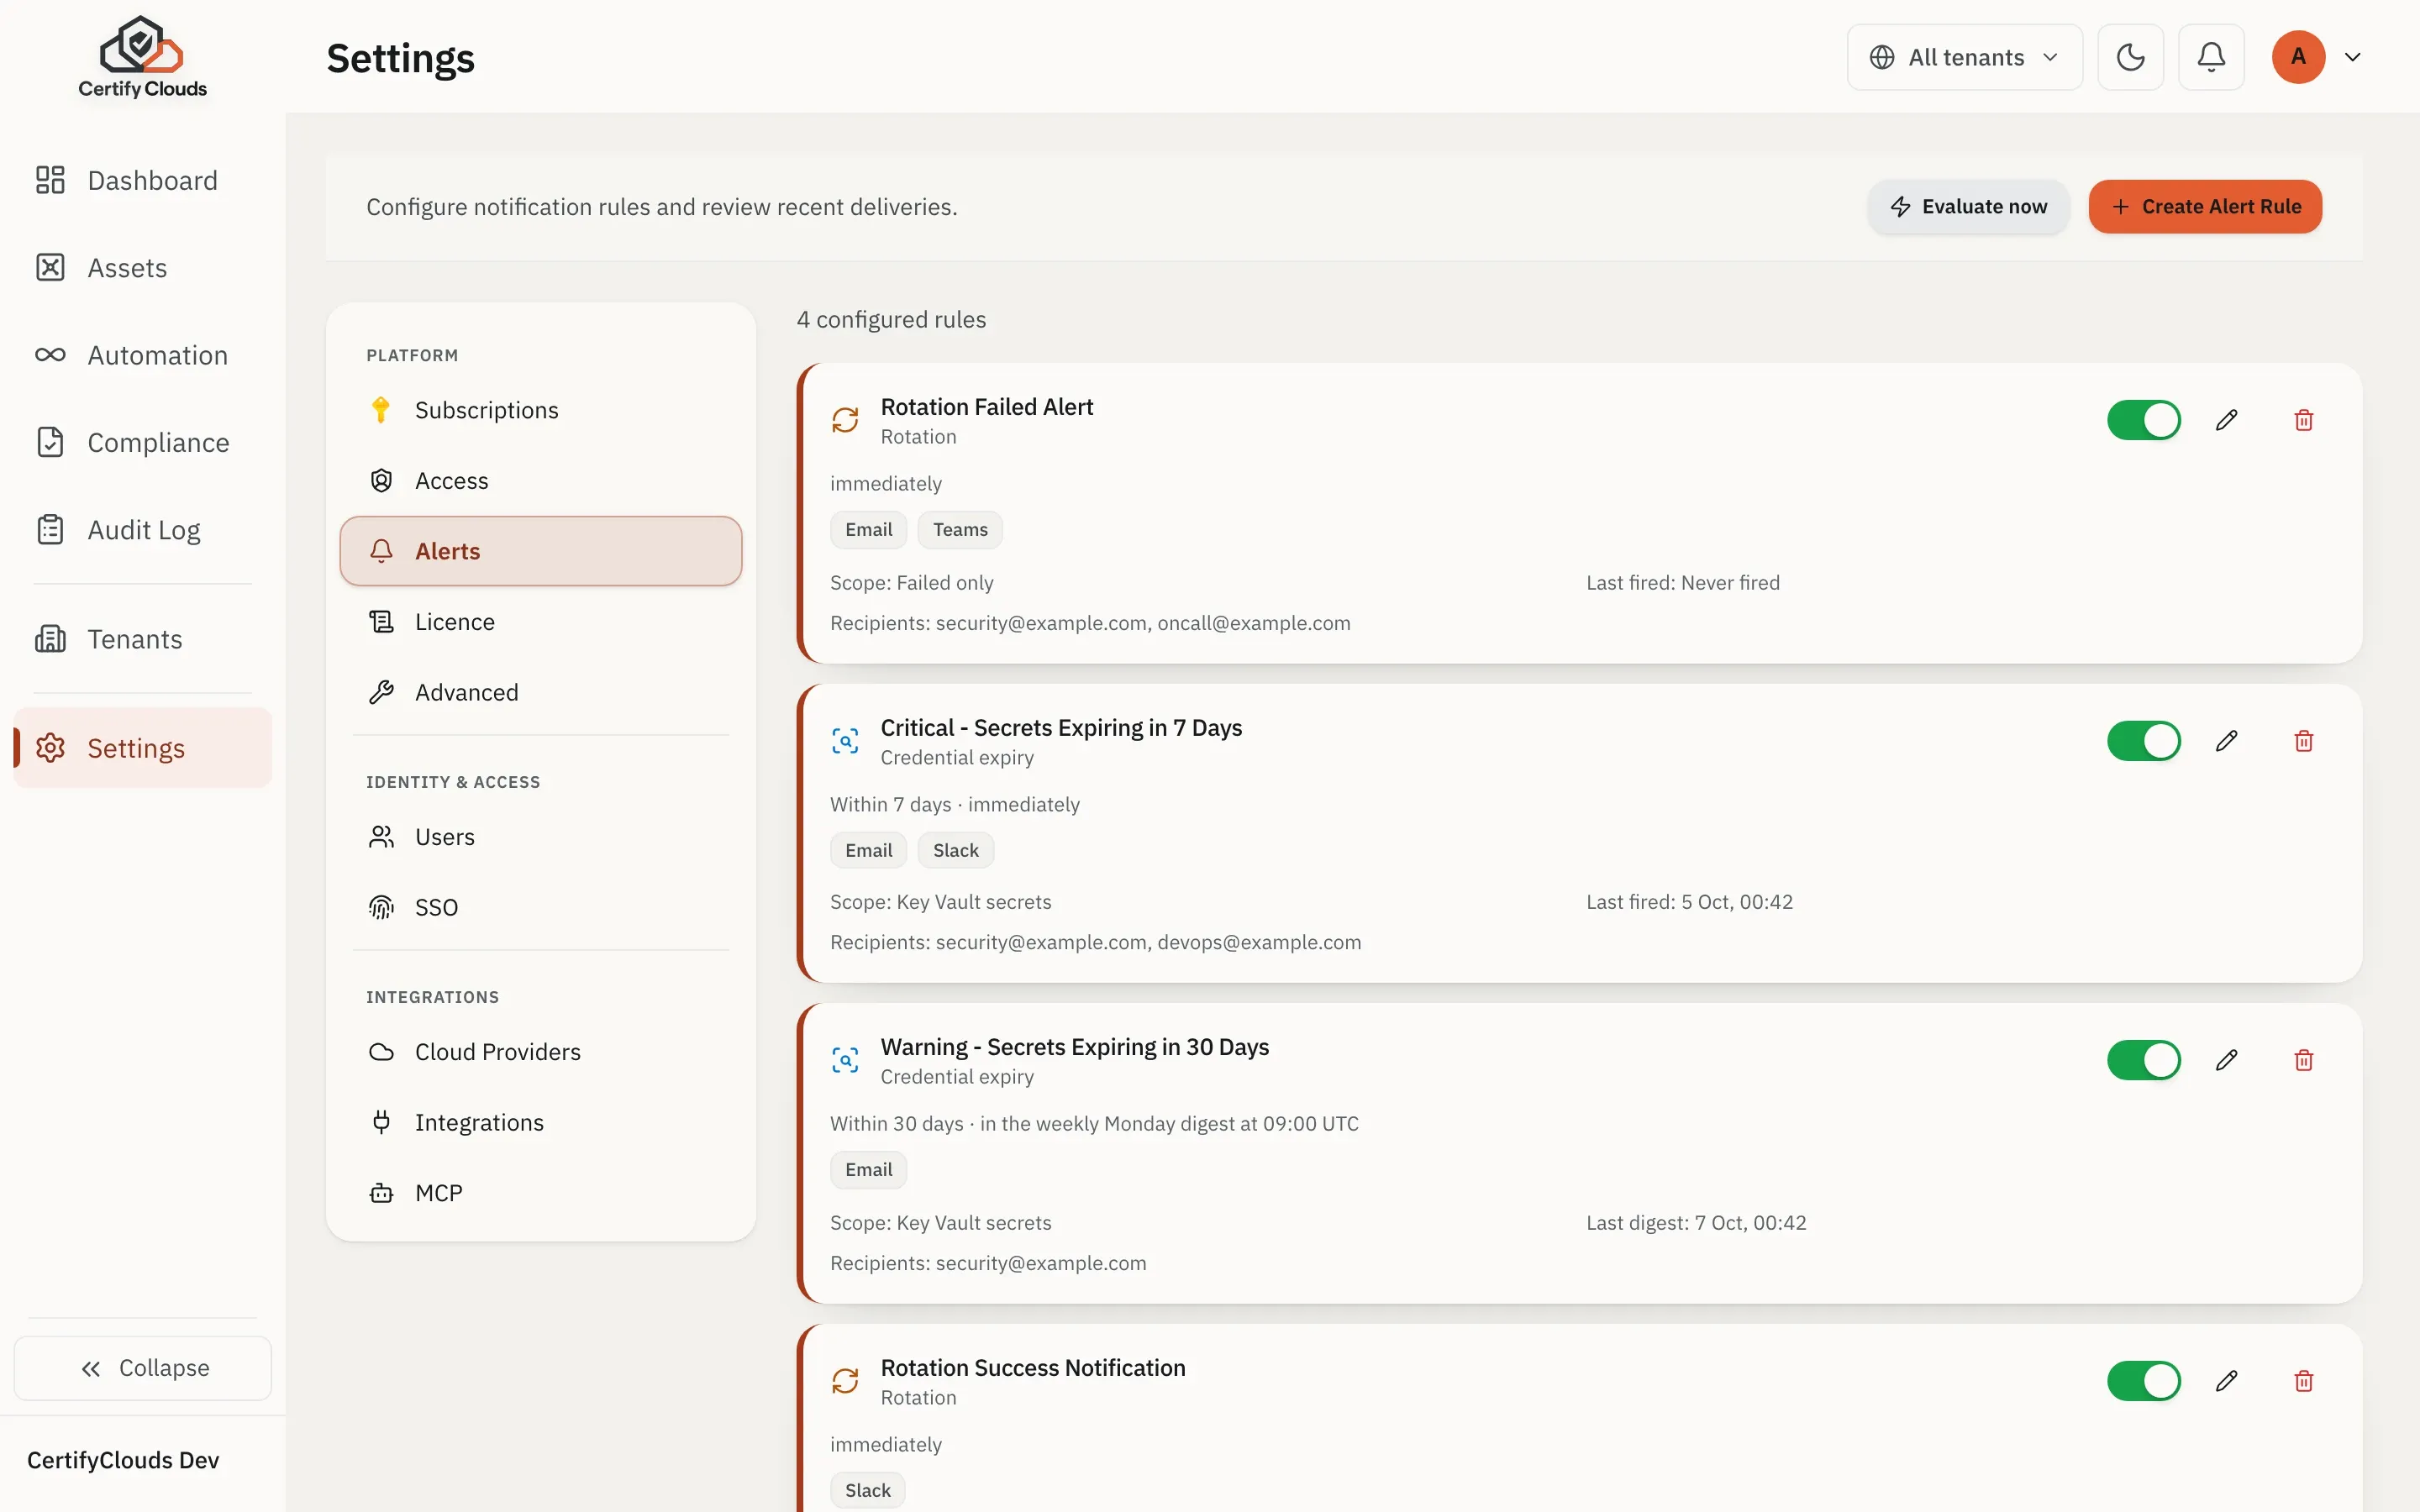
Get notified before secrets expire. Email, webhook, or both.
- Thresholds you set for each rule
- Rules for all credentials or one kind, such as Key Vault secrets or TLS endpoints
- Webhook integration for Slack, Teams, PagerDuty
- App owners in Entra emailed too, once an admin switches it on
- Warns your admins before CertifyClouds' tenant and SSO secrets expire
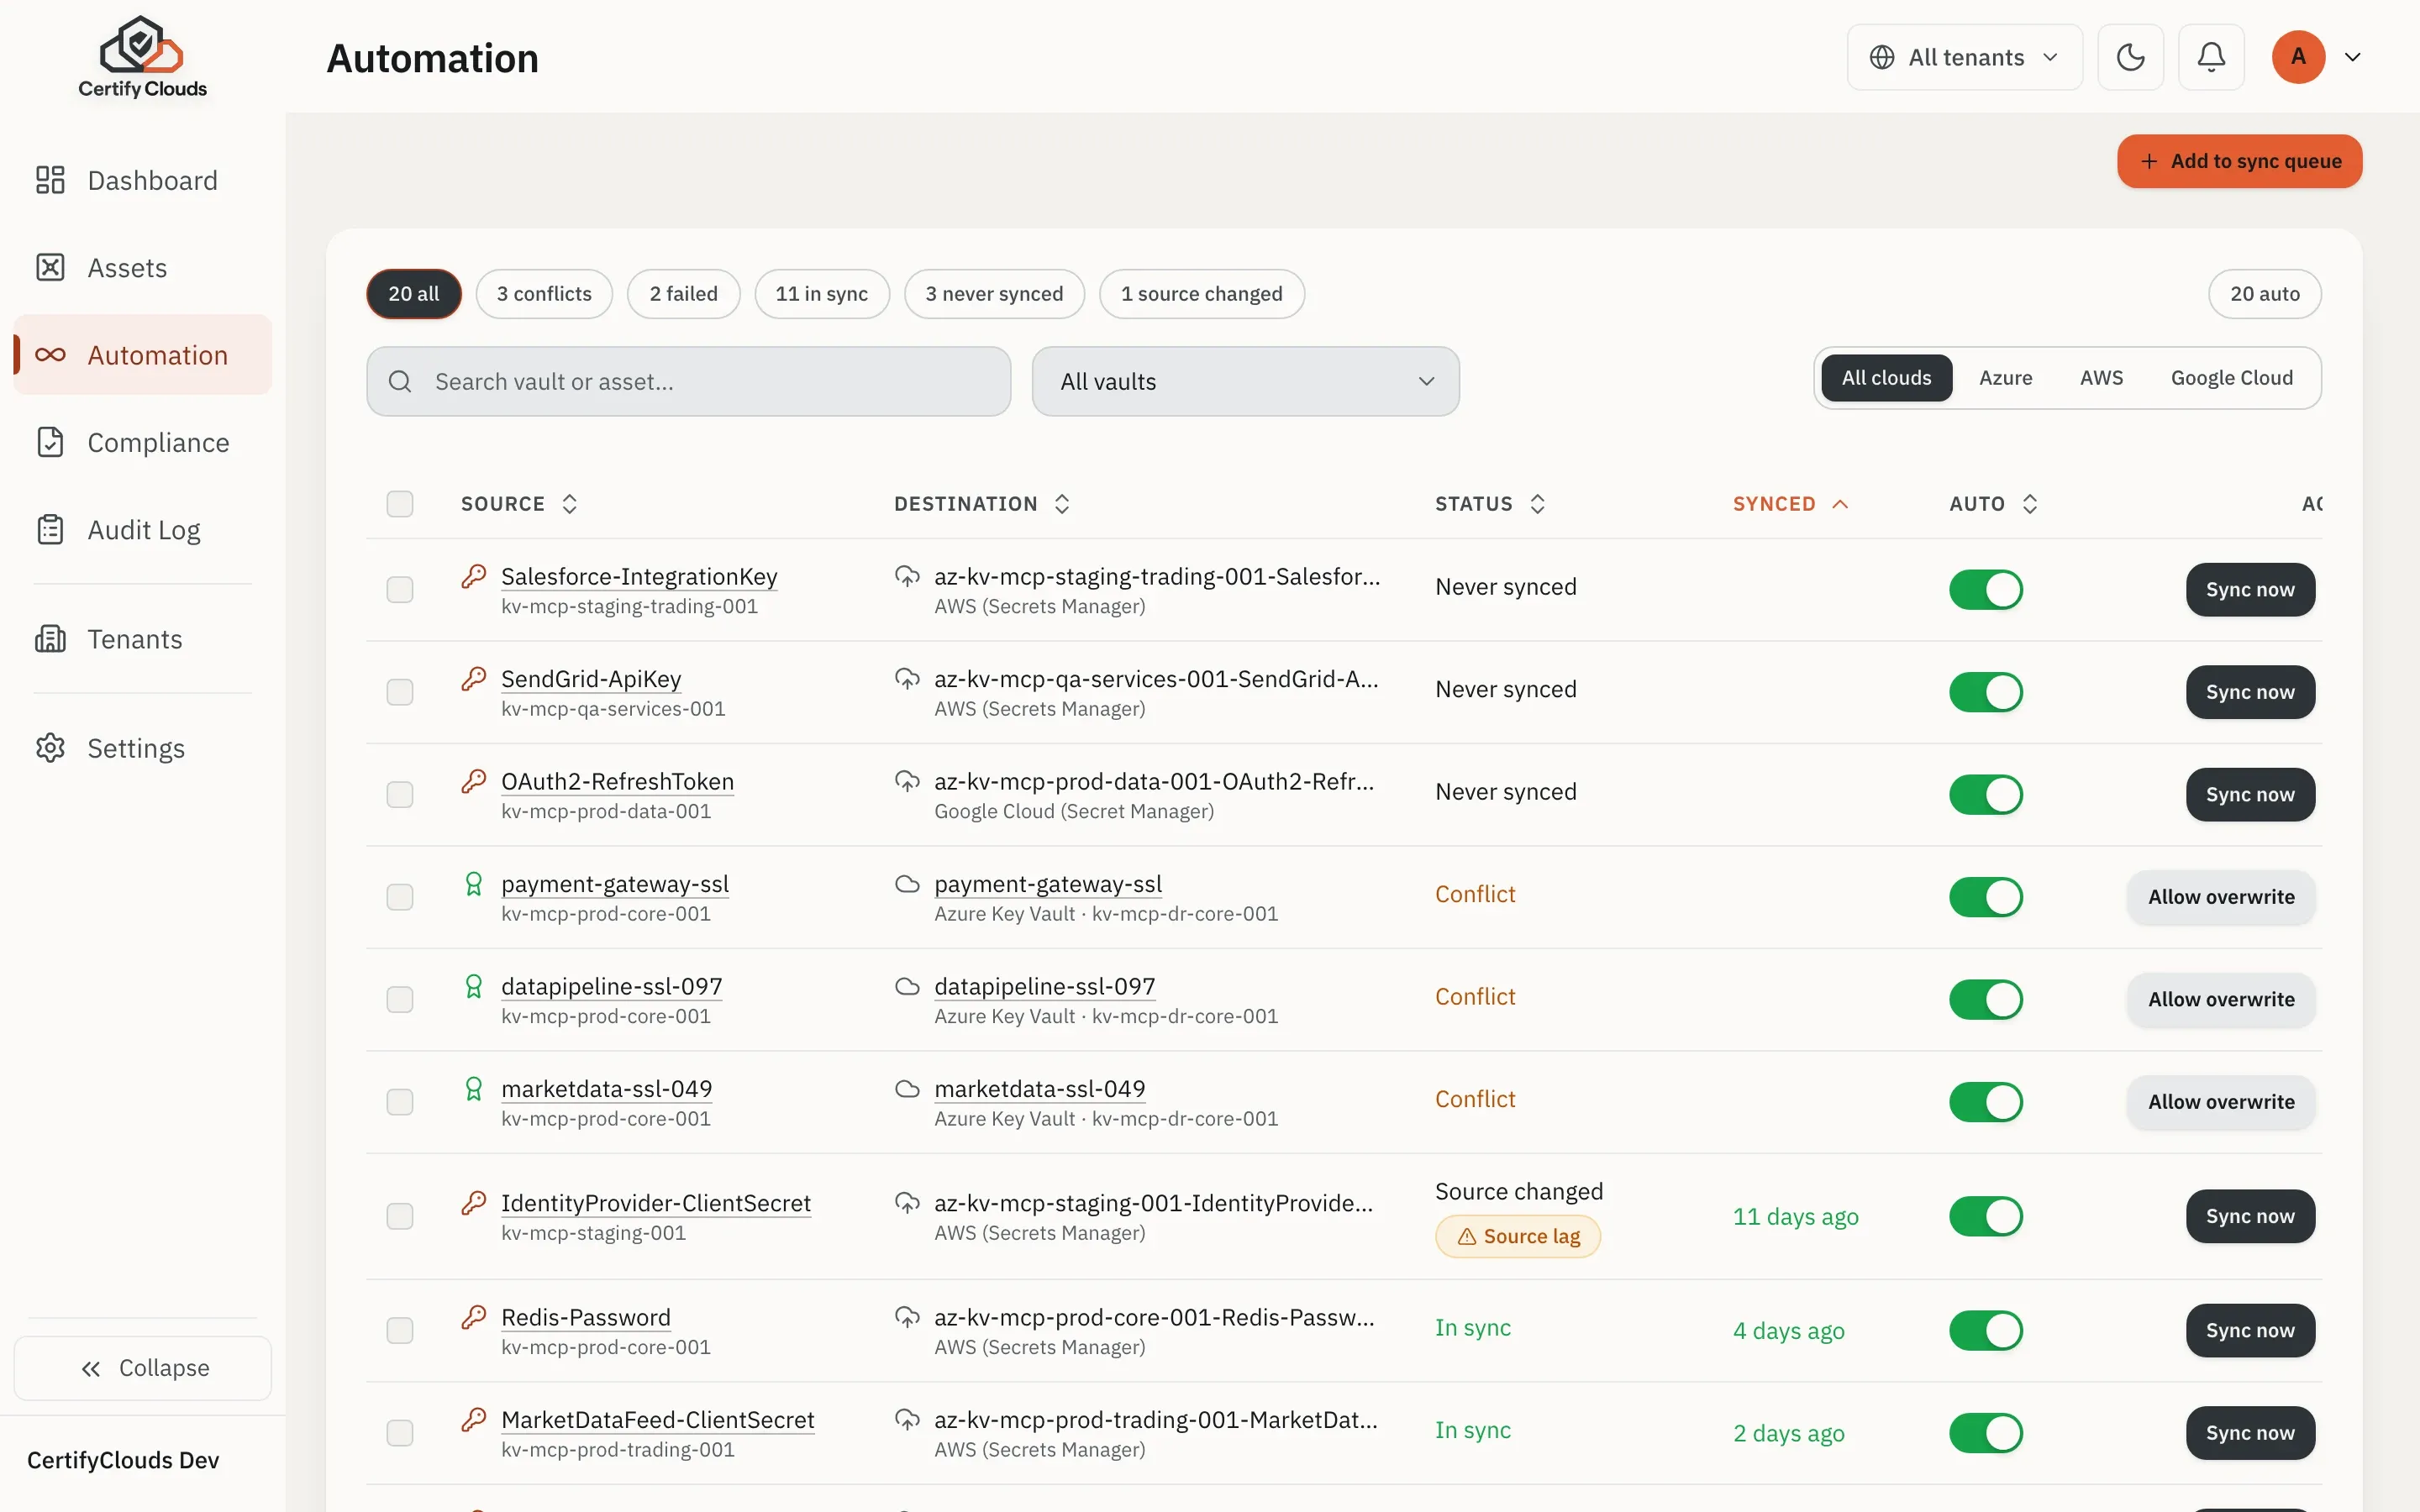
Multi-Cloud Disaster Recovery
Replicate Azure Key Vault secrets and certificates to AWS and GCP secret and certificate managers. When Azure goes down, your DR environment has the credentials it needs.
- Sync to AWS Secrets Manager and ACM
- Sync to GCP Secret Manager and Certificate Manager
- Copies updated straight after every rotation
- The old credential waits for its copies before it is retired, up to a limit you set
- Tag-based secret selection
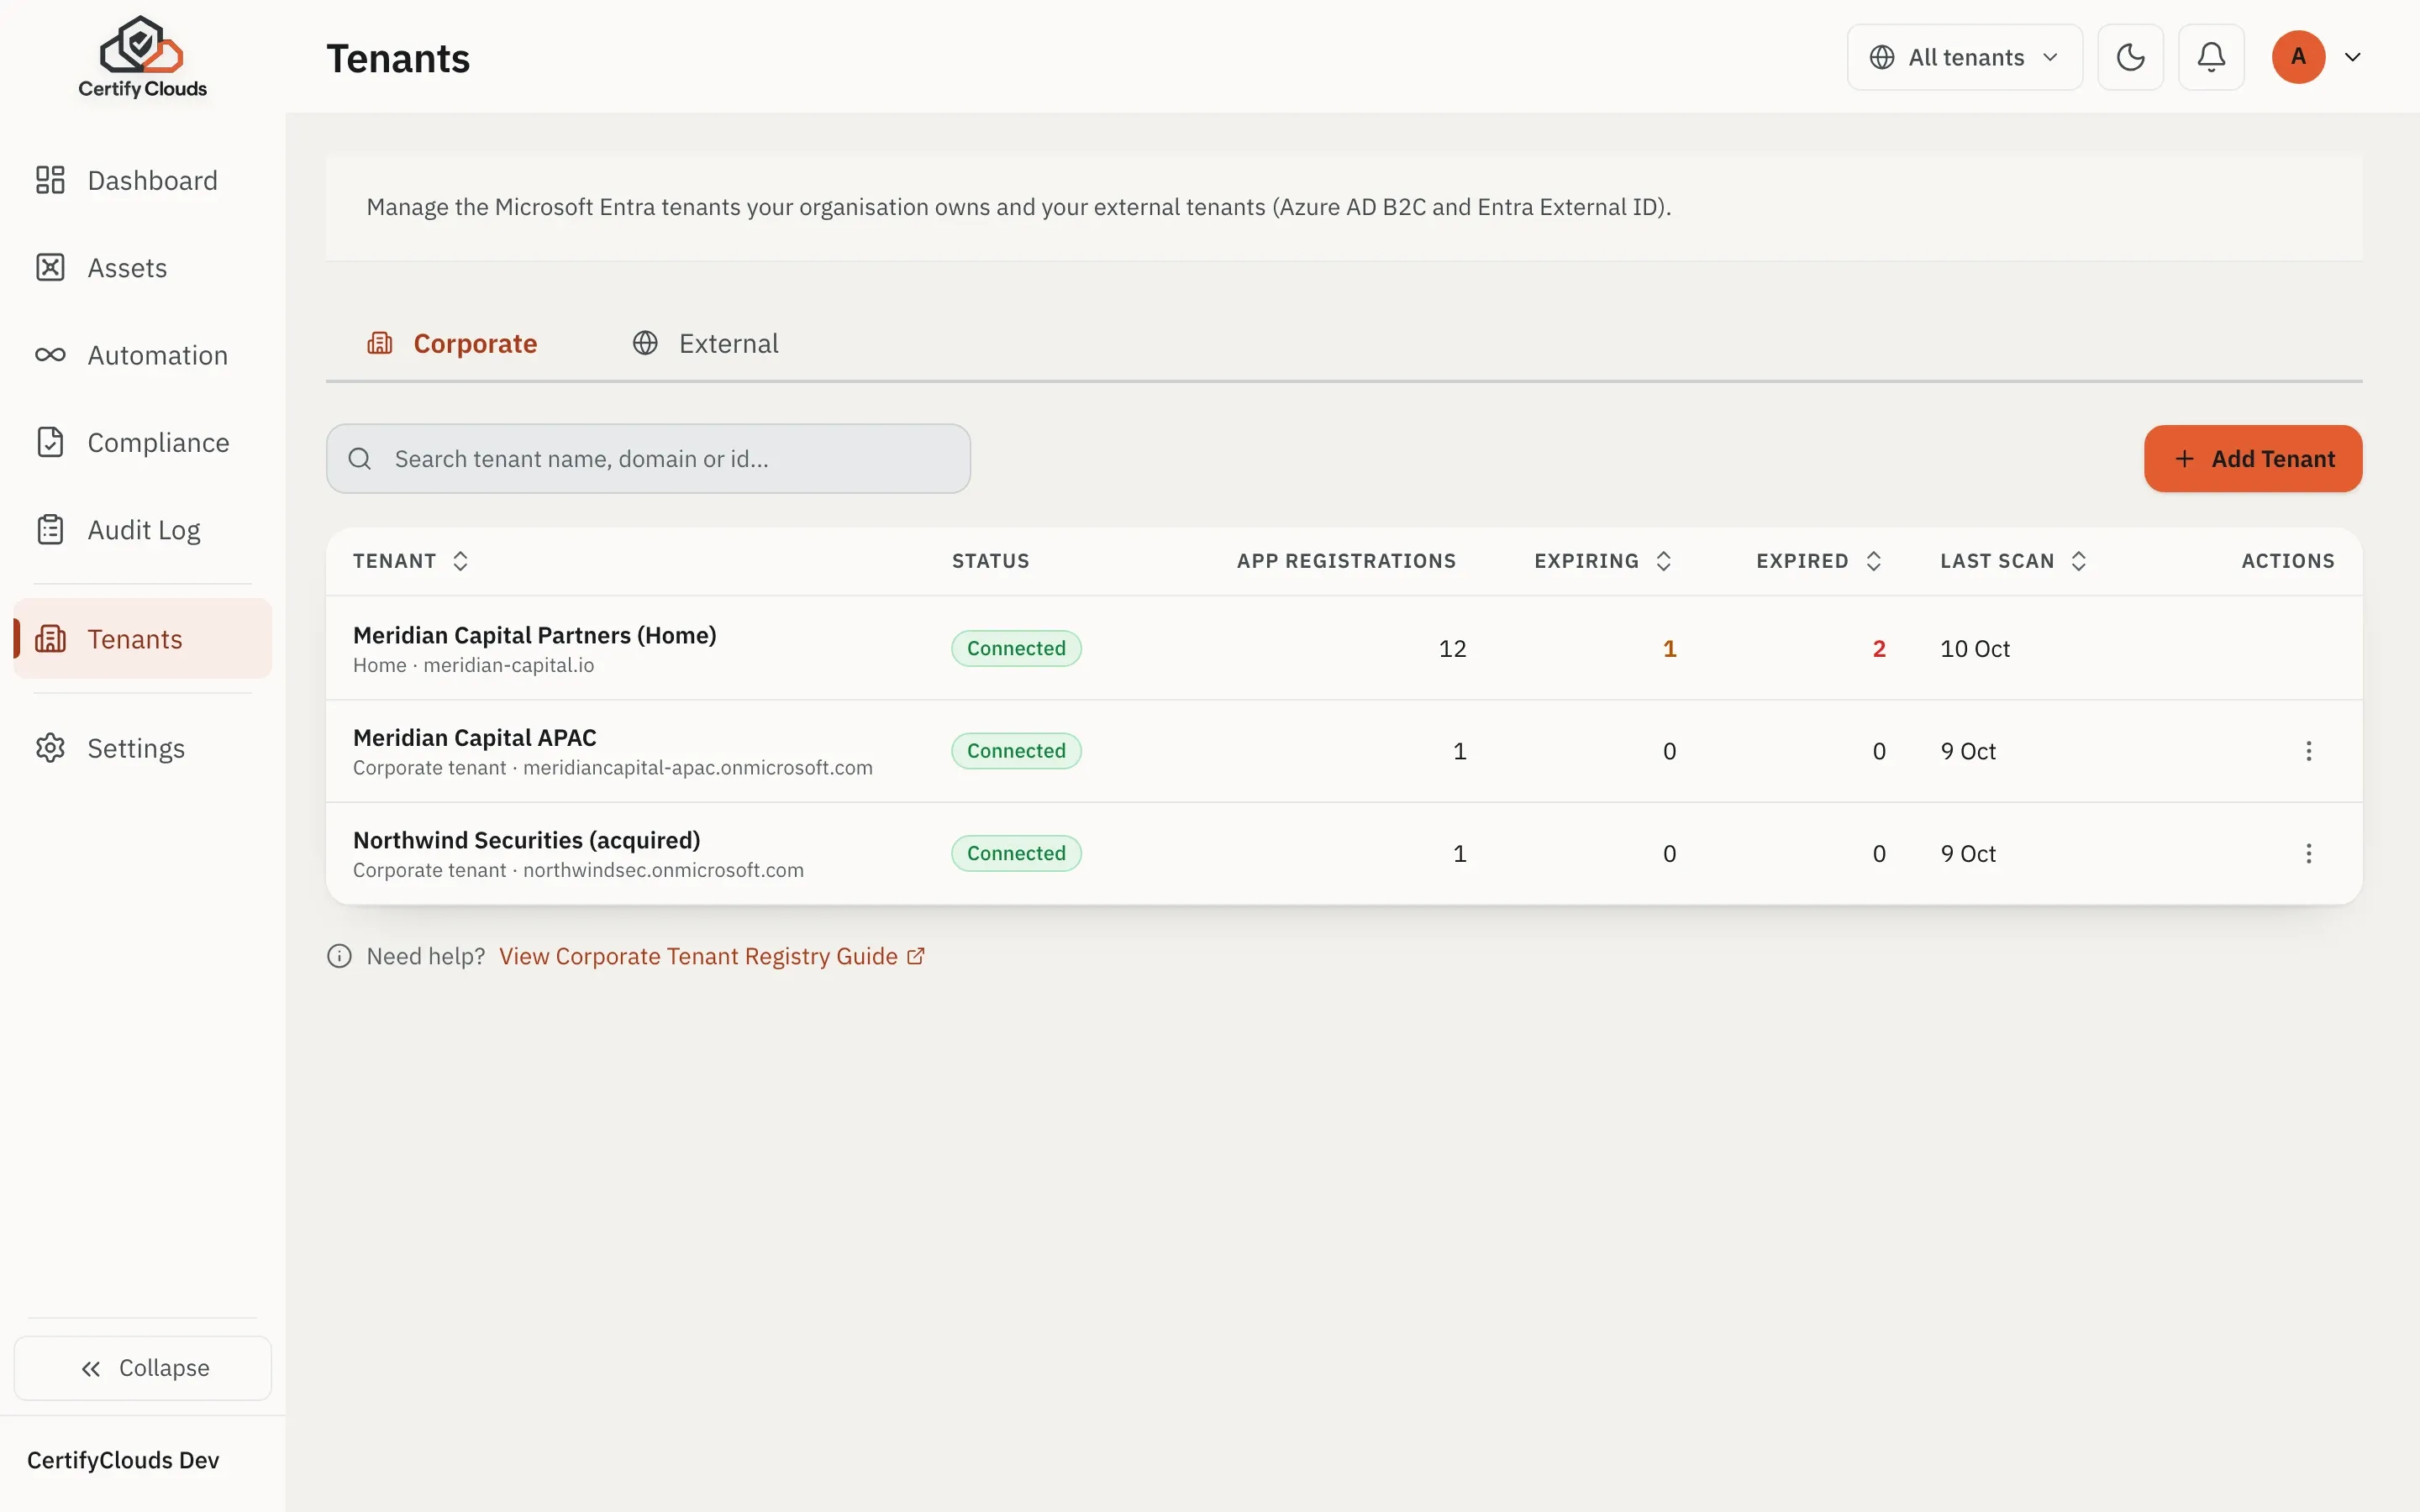
Every Tenant, One Console
MSPs, holding groups, and post-acquisition estates run credentials across many Microsoft Entra ID tenants. Register them all in one CertifyClouds deployment and discover, rotate, and report across the whole estate without switching directories.
- Cross-tenant inventory and rotation from a single console
- Per-tenant connection health and scan status
- Azure AD B2C and Entra External ID tenants alongside your corporate directories
- Key Vault to Key Vault replication for regional DR and environment sync